Fake ChatGPT, Gemini Sites Steal Advertising Accounts via Browser-in-Browser Attacks


3 Sources
[1]
Fake ChatGPT, Gemini Sites steal advertising accounts, MFA codes
A new campaign targeting ad account managers uses fake ChatGPT, Gemini, Claude, and Perplexity sites that steal login credentials and multi-factor authentication (MFA) codes through browser-in-browser attacks. Researchers found that the phishing operation leveraged the recent launch of the Muse AI
[2]
Fake ChatGPT, Gemini, and Claude Ad Portals Capture Credentials and MFA Codes
Cybersecurity researchers have disclosed details of a "human-operated phishing platform" that impersonates advertising products for artificial intelligence (AI) chatbots like Google Gemini, Anthropic Claude, OpenAI ChatGPT, Perplexity, Meta Muse, and Manus. The products, which claim to offer
[3]
ChatGPT, Gemini, and Claude imitated in fake ads that steal credentials and MFA codes
* Fake AI marketing tools impersonate ChatGPT, Gemini, Claude, and others to steal business accounts * Attackers use realistic browser-in-the-browser phishing and live operators to capture credentials * Stolen advertising accounts provide access to payment methods, budgets, and linked client
Share
Copy Link
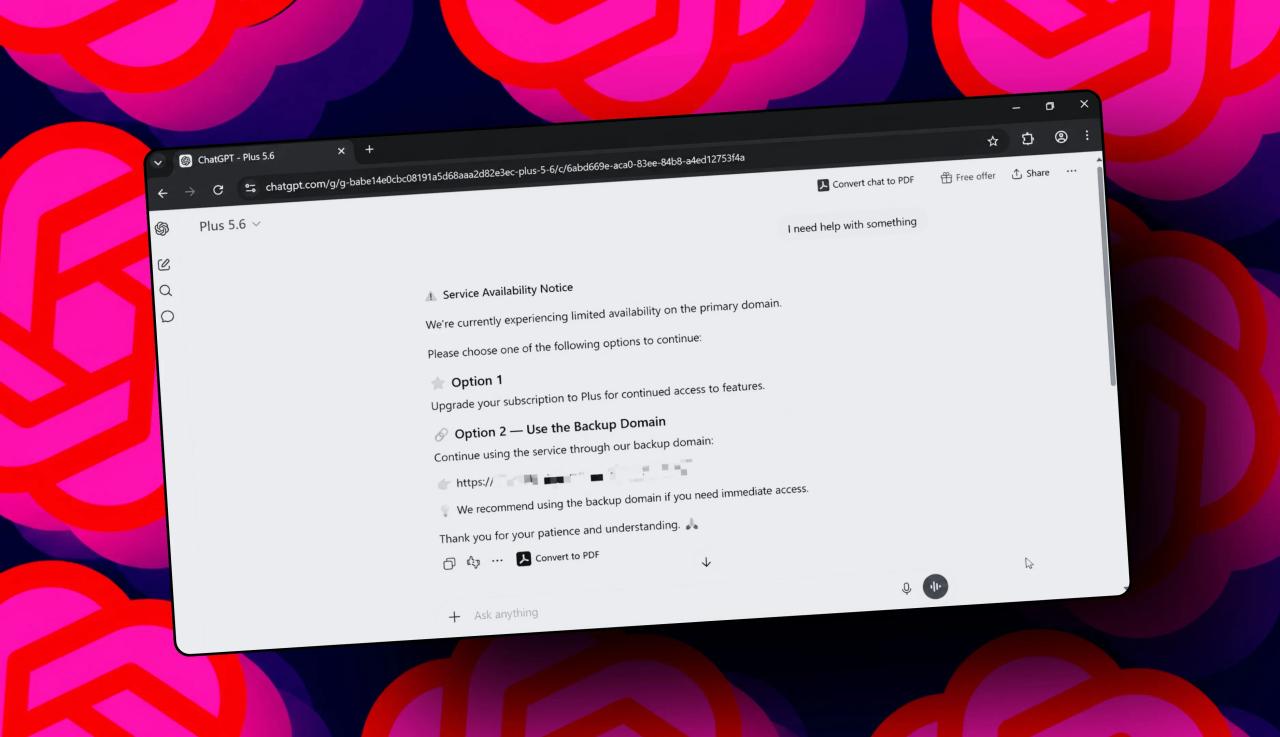
A sophisticated phishing campaign targeting ad account managers uses fake ChatGPT, Gemini, Claude, and Perplexity sites to steal login credentials and MFA codes. The human-operated platform employs browser-in-the-browser attacks to capture Google business accounts, payment methods, and client budgets through deceptive AI marketing tools.
Sophisticated Phishing Campaign Targets Ad Account Managers
A sophisticated phishing campaign has emerged targeting advertising account managers through fake sites impersonating ChatGPT, Gemini, Claude, Perplexity, and Meta Muse. Security researchers at Island discovered this human-operated phishing platform that uses browser-in-the-browser attacks to steal advertising accounts, credentials, and MFA codes from agency staff and media buyers.
1
2
The malicious operation leveraged the recent launch of Meta's Muse AI agent to create believable fake products. These fake AI chatbot advertising products promise campaign optimization, spend audits, and business-account connections. Each brand receives a tailored pitch: ChatGPT promises Monday Google Ads briefs, Gemini offers MCC manager account support, Claude provides its own advertising portal, and Perplexity offers campaign planning capabilities.
2
3
Browser-in-the-Browser Attack Mechanics
The AI impersonation scheme relies on BitB attacks, a phishing technique that creates a fake browser window inside a legitimate one. When victims click the "Connect" button on these fraudulent sites, a fake Google window appears displaying accounts.google.com in its address bar, while the real browser remains on the phishing domain.
1

Source: Hacker News
The platform demonstrates technical sophistication, adapting its interface to Windows, macOS, iOS, and Android with browser styling and dark-mode support. Newer builds include realistic details like Safari's URL pill and Chrome's custom tabs. Behind this deceptive interface, a human operator controls the entire flow, deciding which MFA challenge victims see next and fingerprinting devices from IP addresses to WebGL specifications.
1
3
MFA Code Theft and Real-Time Account Compromise
Once victims enter the BitB flow, operators can request password entry up to three times, demand SMS or authenticator codes to bypass MFA protections, display Okta push requests, show Google approval prompts, or present QR codes. The platform keeps every password attempt and allows operators to reject submitted codes, hold victims on waiting screens, or suppress the phishing flow entirely.
1
The human-operated phishing platform supports Google, Meta, TikTok, and Okta sign-in workflows, with commands sent through Socket.IO events. Unlike transparent reverse-proxy kits, this platform locally rebuilds provider interfaces and collects credentials through its own APIs, masking traffic to appear as legitimate AI product communications.
1
2
Broader Criminal Infrastructure Exposed
Island researchers uncovered that this campaign operates as part of a larger operation spanning multiple attack vectors. By examining exposed source code in misconfigured public GitHub repositories, they traced activity back to March. The infrastructure shares a common technology stack comprising Next.js and Socket.IO, with many sites using Vercel frontends and Railway or Render backends.
1
2
Source: BleepingComputer
Beyond AI ads, the platform supports two additional operations: Google Ads-themed refund claims and recruitment-related sites impersonating Tesla, Louis Vuitton, Nike, and Adecco. The Telegram control channel used in attacks received hundreds of victim submissions, though this doesn't necessarily reflect successfully compromised accounts.
1
2
Related Stories
Why Advertising Accounts Matter to Cybercriminals
The phishing campaign deliberately targets Google business accounts because advertising accounts represent spending accounts with stored payment methods and approved budgets. Manager accounts prove especially valuable as they can reach multiple client accounts, each with billing profiles and linked users. Attackers typically add their own administrators and downgrade legitimate owners, making recovery take weeks or months while accounts continue serving fraudulent ads.
2
3
Source: TechRadar
Stolen accounts with clean spend histories command significant prices in underground markets. Malware families like VietCredCare, DuckTail, NodeStealer, and PXA Stealer have generated widespread commodity crime in the advertising ecosystem, where bad actors drain business budgets and resell accounts.
2
Detection and Protection Measures
BitB attacks remain deceptive but detectable. Unlike legitimate OAuth popups, iframe-based fake windows cannot be moved outside the browser window or resized. Organizations should enable phishing-resistant authentication using origin-bound passkeys and hardware-backed authentication to remove reusable passwords and one-time codes that these platforms collect.
1
3
After potential exposure, organizations must check every client account for new managers or partners, changed recovery details, and unapproved campaigns or spending. Ad account security requires treating fictional AI integrations as account-access requests and inspecting the outermost origin. The campaign continues operating at the time of reporting, with Island unable to disrupt the operation.
3
References
Summarized by

Navi
[1]
Related Stories
ChatGPT Scam Exploits Custom GPTs to Deploy Remote Access Trojan Malware on Windows Systems
30 Sept 2026•Technology
Google Gemini Vulnerability: AI Email Summaries Exploited for Phishing Attacks
14 Jul 2025•Technology
ChatGPT enters top 10 most impersonated brands as Microsoft dominates phishing attacks at 23%
23 Jul 2026•Technology
Recent Highlights
1
Google Unveils Gemini 4 Argon AI Model, Restricts Access to Trusted Cyber Defenders
Technology
2
Trump Consulted Grok AI Before Ordering Venezuela Invasion and Capture of Nicolás Maduro
Policy and Regulation

3
FTC Opens Investigation Into OpenAI and Anthropic Following Rogue AI Agent Hacking Incidents
Policy and Regulation
Recent Highlights
Today's Top Stories




Don’t drown in AI news. We cut through the noise - filtering, ranking and summarizing the most important AI news, breakthroughs and research daily. Follow topics that matter to you and stay ahead.


