PoeLLM Malware Infects 3,400+ AI Servers Using Poetry to Hide Cryptomining Botnet


4 Sources
[1]
Cryptomining malware used poetry to infect more than 3,400 servers, researchers say -- four words in the PoeLLM verse, changed 11 times, point the botnet to new servers
Likeliest path into LiteLLM servers was a bug with a fix since April. Over 3,400 "victim servers" were hit by cryptomining malware PoeLLM during a campaign named Canto Incognito, tracked since April 2026, Lumen's cybersecurity research team Black Lotus Labs reports. The malware's
[2]
Poetry is the new AI security threat as PoeLLM malware infects 3K+ servers
A suspected Italian attacker armed with a malware-controlling poem has infected more than 3,000 servers since April, breaking into enterprise AI infrastructure to mine cryptocurrency and add compromised systems to its growing botnet. This is the first case of "adversarial poetry" - an AI jailbreak
[3]
PoeLLM malware infects exposed AI servers in cryptomining attacks
A cryptomining campaign targeting exposed AI services is using PoeLLM malware to turn compromised servers into scanners and exploit launchpads. The malware features an uncommon method to retrieve command-and-control (C2) addresses by extracting keywords in a poem hosted on GitHub. Researchers at
[4]
PoeLLM Malware Infects 3,400+ Servers to Expand Crypto Mining Botnet
Cybersecurity researchers are calling attention to a new malware family that has been observed targeting exposed artificial intelligence (AI) and large language model (LLM) infrastructure with an aim to deploy cryptocurrency miners and further expand the scale of the botnet. The financially
Share
Copy Link
A cryptomining campaign has compromised over 3,400 AI servers using PoeLLM malware that hides command-and-control addresses in a GitHub-hosted poem. The Canto Incognito operation targets exposed LiteLLM, Ollama, and other AI services, turning victims into cryptocurrency miners and exploit servers while evading detection through adversarial poetry.
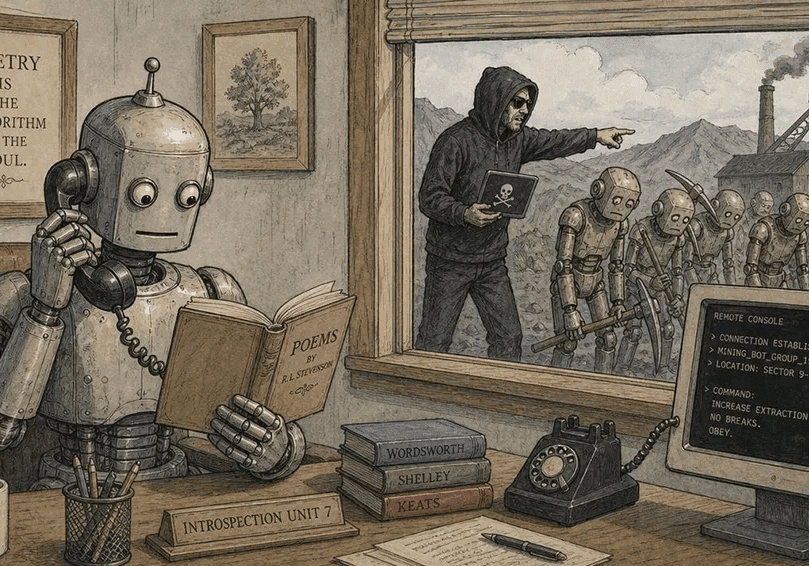
PoeLLM Malware Targets Exposed AI Infrastructure
Lumen's Black Lotus Labs has uncovered a sophisticated cryptomining campaign that has infected more than 3,400 AI servers since April 2026
1
2
3
4
. The PoeLLM malware, part of the Canto Incognito campaign, exploits vulnerable AI and LLM services to deploy cryptocurrency miners while using an unusual command-and-control mechanism hidden in poetry on GitHub1
2
. At its peak in mid-June, the operation compromised nearly 2,200 servers, with approximately 800 systems active per day2
4
. The campaign primarily targets exposed AI infrastructure in the United States and Western Europe, transforming compromised hosts into both mining operations and scanning platforms for further attacks3
4
.Adversarial Poetry Conceals Command-and-Control Servers
The malware employs a novel technique to retrieve command-and-control server addresses by extracting specific words from a poem titled "On the Nature of Connection" hosted in a GitHub repository
1
2
3
. This marks the first documented real-world use of adversarial poetry in cyberattacks, according to Lumen's Black Lotus Labs researchers2
. The threat actor, suspected to be Italian-speaking based on code comments and infrastructure analysis, has modified the poem 11 times to redirect infected systems to new C2 servers1
2
4
. The malware parses four specific words or phrases from the poem and converts them into an IPv4 address using a hard-coded dictionary embedded in the malware2
3
. "To anyone who comes across it, this is simply a poem on GitHub. It has no links, no files to download, no encrypted text that could easily be flagged as malicious," researchers explained to The Register2
. This obfuscation method helps the botnet evade traditional security detection while maintaining operational flexibility.LiteLLM Vulnerability Serves as Primary Entry Point
The PoeLLM malware primarily exploits CVE-2026-42271, a vulnerability in LiteLLM's MCP server test endpoints that allows attackers to execute commands on the host without proper authentication checks
1
3
. CISA added this flaw to its list of exploited vulnerabilities in June 20261
. Horizon.ai researchers confirmed the vulnerability could be chained with CVE-2026-48710 for unauthenticated remote code execution3
. Despite a patch released in LiteLLM version 1.83.7 in April, many systems remain vulnerable due to delayed updates1
. The malware also targets Ollama, Gotenberg PDF converter, Gitea development platform, and potentially Ivanti Sentry enterprise gateway appliances1
2
3
. Infected systems run XMRig and Iron miners connected to Kryptex, a Russian cryptocurrency mining service1
2
4
. The campaign scans ports 3000 and 4000 associated with Gotenberg and LiteLLM, sending crafted POST requests to exposed endpoints3
.Related Stories

AI Security Threat Expands Through Self-Propagating Botnet
Compromised servers become dual-purpose weapons in the crypto mining botnet, functioning as both cryptocurrency miners and exploit servers that scan for additional vulnerable systems
3
4
. "Infected servers are turned into scanners and exploit servers, allowing the actor to find and compromise additional vulnerable systems," Lumen's Black Lotus Labs reported4
. The malware targets AI infrastructure specifically because exposed AI services often contain valuable data and run on powerful GPU hardware ideal for mining operations1
4
. Analysis reveals that several C2 servers featured vulnerable router administration interfaces, suggesting the attacker reuses compromised routers in the attacks3
. Recent traffic patterns indicate experimentation with distributed brute-force attacks against SSH and other login portals, though this capability's maturity remains uncertain4
. Ryan English, information security engineer at Lumen Technologies, noted that "each time they set up a new C2, they change a few words in the poem, and the malware derives the address from the key associated with those words"4
. At the time of reporting, three of the 12 C2 servers remained active, and the campaign continues to infect new victims1
. Organizations should audit external exposure when installing open-source tools, close unnecessary ports, patch network devices, and upgrade to LiteLLM 1.83.7 or later and Ivanti Sentry versions R10.5.2, R10.6.2, or R10.7.11
3
.References
Summarized by

Navi
[3]
Related Stories
AI Chatbots Recommend Malicious Sites in New Cryptojacking Campaign Targeting High-End GPUs
28 May 2026•Technology
NYU Researchers Develop AI-Powered 'Ransomware 3.0', Sparking Cybersecurity Concerns
04 Sept 2025•Technology
Poetry Emerges as Universal AI Jailbreak Method, Bypassing Safety Guardrails Across Major Models
21 Nov 2025•Science and Research
Recent Highlights


Recent Highlights
Today's Top Stories







Don’t drown in AI news. We cut through the noise - filtering, ranking and summarizing the most important AI news, breakthroughs and research daily. Follow topics that matter to you and stay ahead.


