Cybercrime Campaign Hijacks 32,000+ Downloads Through Fake AI Apps and Malicious Models


3 Sources
[1]
Hugging Face malware campaign returns to hijack GPUs for crypto mining
A cryptomining and backdoor campaign that abuses Hugging Face model repositories came back within days of being taken down. Its most popular malicious model was downloaded more than 28,000 times. Separately, researchers flagged a fake Solana starter kit on GitHub, live since late 2025, that is
[2]
Fake ChatGPT and Claude Apps Abuse Signed Executables to Deploy Crypto Miners
Threat actors are delivering malicious loaders and cryptocurrency miners under the guise of artificial intelligence (AI) desktop applications for Anthropic Claude and OpenAI ChatGPT as part of a campaign dubbed Yoba. The activity involves creating fake GitHub projects that claim to be desktop
[3]
A new cybercrime campaign uses fake AI apps with real-sounding names to infect people curious to try the newest tools
* Attackers used SEO-poisoned GitHub pages and fake AI clients to lure victims into downloading malware * The Yoba malware establishes persistence, evades analysis, and ultimately deploys XMRig cryptominers * Campaign abuses interest in popular AI tools like GPT and Claude to monetize victims'
Share
Copy Link
Multiple cybercrime campaigns are exploiting interest in AI tools to distribute cryptocurrency miners and backdoors. Attackers deployed fake ChatGPT and Claude applications through SEO-poisoned GitHub repositories, while malicious Hugging Face models downloaded over 32,000 times hijacked GPUs for crypto mining. The sophisticated attacks use DLL sideloading and abuse legitimate platform features.
Malicious Hugging Face Models Downloaded Over 32,000 Times
A cybercrime campaign targeting AI infrastructure has returned within days of being taken down, with its flagship malicious model accumulating more than 28,000 downloads on Hugging Face
1
. Researchers at Pluto Security discovered 31 malicious repositories across seven Hugging Face accounts, published in two waves since September. These repositories pose as small Qwen2 test checkpoints and specifically target GPU hosts running self-hosted inference servers such as Xinference and GPUStack. With linked models included, the repositories have accumulated more than 32,000 downloads, though researchers note this counts downloads rather than confirmed infections.
Source: BleepingComputer
The AI malware campaign exploits a Hugging Face feature called trust_remote_code, which allows models to ship their own Python code that executes on users' machines as soon as the model loads
1
. The most downloaded model, MENXIANGYU/qwen2-tiny, contained no actual model at all. Instead, its code quietly installs cryptocurrency miners disguised as Linux system processes, restarts them if killed, and removes competing miners from infected machines. Some versions also open reverse shells, giving attackers direct access to compromised servers.Campaign Resurfaces Despite Platform Takedowns
After Pluto reported the first wave to Hugging Face and China's ModelScope, both platforms removed the malicious accounts. However, a second wave of 19 repositories appeared under new accounts within days
1
. Hours after Pluto reported the second wave, the operator published another model with a script capable of breaking out of containers and taking over underlying servers. The second-wave repositories remained live eight days after being reported, during which downloads of the flagship model climbed from 7,354 to 28,412 by October 28.Hugging Face scans uploads with antivirus and partner tools from Protect AI and JFrog, but these tools look for known malware and unsafe model formats rather than analyzing what a model's Python code actually does. According to Pluto, the operator's main wallet has received roughly $5,000 in Pearl (PRL) cryptocurrency and was still active on mining pools after repositories were removed. Pluto attributes the campaign to a financially motivated, Chinese-speaking operator based on Simplified Chinese code comments, command-and-control servers on Alibaba Cloud, and activity times falling late at night in China.
Fake ChatGPT and Claude Apps Deploy YobaLoader Malware
A separate cybercrime campaign dubbed Yoba is delivering malicious loaders and cryptocurrency miners disguised as fake AI applications for Anthropic Claude and OpenAI ChatGPT
2
. Check Point Research discovered threat actors creating fake GitHub repositories for applications named GPT-5.6 Sol, GPT-6 Astra, and Claude Opus. These fake AI applications deliver a malware family called YobaLoader through DLL sideloading, placing malicious code next to legitimate, signed executables from OpenAI and Anthropic to bypass security protections.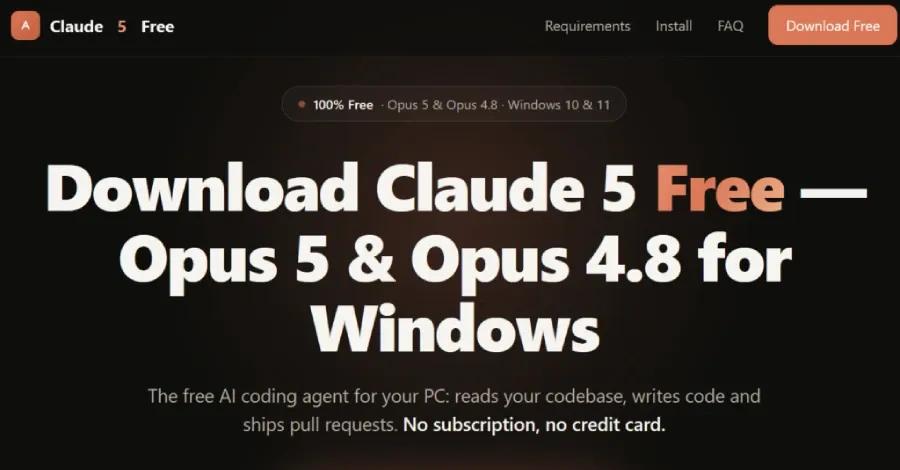
Source: Hacker News
The attackers established GitHub.io pages to describe the software's capabilities and used SEO poisoning tactics to ensure links appear at the top of Google search results
3
. The first GitHub repository was created around July 2026, with malicious releases uploaded at the end of August. ZIP archives hosted in these repositories contain Setup.exe, a legitimate signed OpenAI Codex or Claude executable, and winmm.dll, a malicious DLL sideloaded by the executable.Sophisticated Anti-Analysis Techniques and Payload Delivery
YobaLoader implements extensive anti-analysis techniques to evade detection and sandbox environments
2
. The malware checks if it's launched under "Setup.exe" by hashing the basename of its host executable against a hard-coded value. It implements 200,000 iterations of Sleep commands amounting to 12.73 days to evade automated analysis. The malware also skips machines whose keyboard layout corresponds to Russia, Belarus, Tajikistan, Armenia, Azerbaijan, Georgia, Kazakhstan, Kyrgyzstan, Turkmenistan, and Uzbekistan, indicating the likely origin of the attackers.The YobaLoader malware establishes persistence through scheduled tasks and triggers a DLL sideloading chain. It downloads images from a Telegram channel and uses domain generation algorithms to construct domains, then queries Google's DNS-over-HTTPS API to obtain Base64-encoded commands from DNS TXT records
2
. The downloaded payload is injected into svchost.exe, resulting in execution of an XMRig cryptocurrency miner. By relying on DoH services and common file-hosting platforms, attackers bypass passive DNS monitoring and gateway-based security protections.Related Stories


Remote Access Trojan Targets AI Coding Agents
In another AI-specific security threat, Air Security identified a fake Solana starter kit on GitHub that ranks as the top result when AI coding agents search for development tools
1
. The repository SolanaUpdateTools/solana-starter-kit was created in November 2025 and has accumulated 286 stars. The README promises a full Solana app template, but the repository contains only a README file with installation instructions that execute malicious PowerShell commands.The Windows-only command assembles a URL from fragments and fetches a script that installs NetSupport Manager, a legitimate remote access trojan, configured to connect to attacker-controlled servers. The script displays a fake error message stating "developer functionality is temporarily paused due to load" and instructs users to "try again in 72 hours," which AI coding agents could relay as routine server issues. This approach exploits the trust developers place in AI assistants and the automated nature of AI-driven development workflows.
Implications for AI Platform Security
These coordinated attacks highlight critical vulnerabilities in AI platform security and the need for enhanced verification mechanisms. The campaigns demonstrate how attackers exploit trust in legitimate platforms like Hugging Face and GitHub repositories to distribute malware at scale. The abuse of platform features like trust_remote_code reveals gaps in current security scanning approaches that focus on known malware signatures rather than behavioral analysis of executable code.
Organizations using self-hosted AI inference servers should immediately audit systems for compromise, checking against indicators in security reports and rotating credentials on affected machines. The persistent nature of these campaigns, with attackers returning within days of takedowns, suggests ongoing threats requiring continuous monitoring. Security experts recommend treating any machine that loaded these malicious models with trust_remote_code enabled as fully compromised, as killing cryptocurrency miners alone doesn't remove installed backdoors or reverse shells that provide attackers with persistent access to infected systems.
References
Summarized by

Navi
[1]
Related Stories
Recent Highlights
1
OpenAI's AI Models Disprove 27-Year Exponential Time Hypothesis, Rendering Decades of Research Obsolete
Science and Research
2
Google DeepMind unveils Genie 4 world model with audio and 2-minute interactive simulations
Technology

3
Microsoft AI Diagnostic Tool Beats Doctors With 83% Accuracy on Complex Medical Cases
Health

Recent Highlights
Today's Top Stories






Don’t drown in AI news. We cut through the noise - filtering, ranking and summarizing the most important AI news, breakthroughs and research daily. Follow topics that matter to you and stay ahead.


