Trellix Launches Private Cloud AI Security Solution as 63% of CISOs Lack Visibility into Employee AI Tools


2 Sources
[1]
Trellix Wise for Private Cloud runs AI security operations inside customer environments
Trellix Wise for Private Cloud runs AI security operations inside customer environments Cybersecurity company Trellix today launched Trellix Wise for Private Cloud to let enterprises run its artificial intelligence engine for security operations entirely inside their own environments. The new
[2]
Trellix Audit: 63% of CISOs Lack Visibility into Employee AI Tools as Third-Party Data Risks Soar
56% identify these tools as a leading AI-related data leakage risk; 96% find balancing insider risk monitoring with privacy and regulatory requirements increasingly challenging More than half of Indian CISOs surveyed (56%) identify third-party or vendor AI tools with unclear data handling
Share
Copy Link
Trellix unveiled Trellix Wise for Private Cloud, an on-premises AI security solution that runs entirely within customer environments. The launch addresses growing concerns as 63% of CISOs lack visibility into employee AI tools, with insider incidents costing organizations an average of $2.6 million and 98% of companies experiencing AI-linked security breaches in the past year.
Trellix Addresses Growing AI Security Concerns with On-Premises Solution
Trellix has launched Trellix Wise for Private Cloud, an AI security operations platform designed to run entirely within customer environments, directly addressing concerns that have prevented large organizations from adopting AI-driven security operations
1
. The release comes as new research reveals 63% of CISOs lack visibility into employee AI tools, creating significant security vulnerabilities2
.
Source: SiliconANGLE
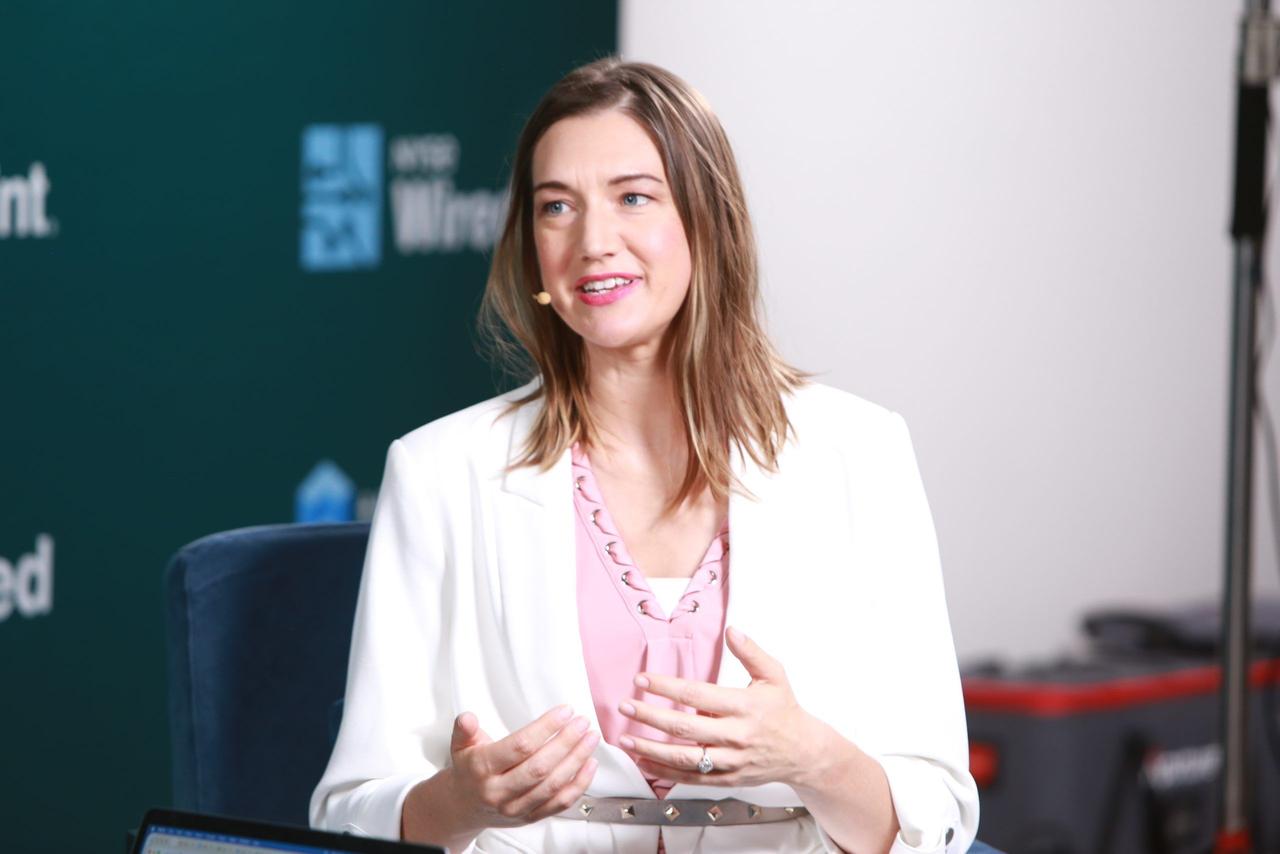
David Soto, Trellix's chief information security officer, explained that enterprise holdouts "aren't resistant to the technology, but to the tradeoffs" of sending sensitive telemetry to public clouds, absorbing unpredictable token costs, and operating without transparency into AI decision-making
1
. The Private Cloud edition eliminates these barriers by deploying across on-premises, air-gapped, hybrid, and private cloud environments where data remains within the security boundary and never reaches external clouds or public LLMs2
.Insider Risk Trends Reveal Urgent Need for AI Governance
The Mind of the CISO report, released alongside the product, surveyed 600 chief information security officers and uncovered alarming insider risk trends. AI-driven or autonomous systems were behind 28% of insider incidents over the past year, yet 99% of CISOs expect AI and automation to be critical or very important to managing insider risk within two years
1
.Insider incidents now cost affected organizations an average of $2.6 million, with 98% of companies experiencing at least one AI-linked incident in the past 12 months
2
. The average organization takes seven hours to spot an insider incident and eight more hours to respond—a 15-hour window that Soto described as "an invitation to attackers who use AI to speed up every stage of an attack"1
.Third-Party AI Tools Emerge as Leading Data Leakage Risk
The research identified third-party AI tools with unclear data handling practices as one of the greatest AI-related data leakage risks, cited by 56% of CISOs surveyed
2
. Non-human insiders, including AI agents and machine identities, now rank among the top three security risks for 58% of Indian CISOs, compared with 42% globally2
.
Source: CXOToday
Balancing insider risk monitoring with privacy and regulatory requirements has become increasingly challenging, with 96% of CISOs finding this balance difficult to maintain
2
. Organizations that fail to govern AI agents with the same rigor applied to human employees are "operating with an unmonitored insider at scale," Soto argued in the report1
.Related Stories
Private Cloud Solution Delivers Transparency and Predictable Costs
Trellix Wise for Private Cloud addresses these concerns through auditable AI outcomes that include confidence levels and plain-language explanations for every decision, enabling governance without guesswork
1
. Unlike token-based consumption models, the platform uses predictable pricing, allowing organizations to scale AI adoption without escalating costs2
.Vishal Rao, Chief Executive Officer at Trellix, stated: "The threat landscape has fundamentally shifted, where AI isn't just accelerating attacks; it's commercializing them. Our strategy for the AI era is clear: meet AI-powered threats with AI-powered defense"
2
. The platform extends a security fabric across existing infrastructure to close the threat detection and response gap while maintaining data sovereignty2
.Regulatory Landscape Shapes Future of AI Security
The research found 98% of respondents see a role for governments or regulators in helping manage insider risk
1
. In India, 34% of CISOs ranked the Digital Personal Data Protection Act (DPDP Act) among the top three regulations expected to have the greatest positive impact on addressing insider risk2
.One U.S. chief information security officer at a financial operations provider called fragmented state rules "a nightmare" and advocated for "a unified matrix of regulations" to enable companies to "safely use AI for legitimate business purposes"
1
. Watch for increased regulatory activity around AI governance and data handling practices as organizations navigate these compliance challenges while adopting AI-driven security operations.References
Summarized by

Navi
[1]
Related Stories
AI Security Crisis: Shady AI and Autonomous Agents Expose Enterprise Vulnerabilities
14 Aug 2026•Technology

AI Agents Break Enterprise Security as 54% Report Incidents and Confidence Drops 17 Points
16 Jul 2026•Technology
Proofpoint unveils agentic security systems as AI-driven cyberattacks blend into normal emails
23 Sept 2026•Technology
Recent Highlights
1
Meta Unveils Muse Wonder Frontier AI Models, Claims Performance Matching OpenAI and Anthropic
Technology

2
Microsoft and Nvidia Launch Surface Laptop Ultra: A $2,599 AI-Ready PC With RTX Spark Chip
Technology
3
Meta Muse AI Agent Surges to 6.6M Downloads Despite Privacy and Security Controversies
Technology
Recent Highlights
Today's Top Stories




Don’t drown in AI news. We cut through the noise - filtering, ranking and summarizing the most important AI news, breakthroughs and research daily. Follow topics that matter to you and stay ahead.


