CrowdStrike 2026 Report: AI Cyberattacks Explode as Hackers Exploit Vulnerabilities in 24 Hours


8 Sources
[1]
AI is both a cyber weapon and a massive target, CrowdStrike warns
Follow ZDNET: Add us as a preferred source on Google. ZDNET's key takeaways * CrowdStrike warns AI is both a target and a weapon. * LLMJacking made nearly 200,000 API calls in two minutes. * Malicious AI exploits flaws faster than defenders can patch them. Artificial intelligence is
[2]
AI is 'both the weapon and the target' in latest wave of cyberattacks
AI is becoming both an attack tool and a high-value target, with attacks by AI-enabled adversaries rising 89 percent in 2025, according to CrowdStrike. The security firm's annual Threat Hunting Report details criminal gangs and nation states using AI throughout the attack chain. Attackers are also
[3]
CrowdStrike finds AI systems under direct attack as exploit windows shrink
Artificial intelligence has become a target for attackers rather than only a tool they use, according to CrowdStrike Holdings Inc.'s "2026 Threat Hunting Report," released today. The annual report draws on observations from CrowdStrike's OverWatch threat hunting team and intelligence analysts
[4]
CrowdStrike 2026 Report Reveals AI-Driven Cyber Threat Surge
CrowdStrike Threat Hunting Report Highlights: Based on frontline intelligence from CrowdStrike's elite threat hunters and intelligence analysts tracking more than 290 named adversaries, the report reveals: AI Is a Tool, Target, and Force Multiplier for Adversaries: Threat actors used AI to
[5]

CrowdStrike 2026 Report: AI Is Now Fully Embedded in Cyberattacks
Threat actors operationalize AI to exploit vulnerabilities within hours, target enterprise AI, and scale attacks across software supply chains CrowdStrike today released the 2026 Threat Hunting Report, revealing that AI is now embedded across modern adversary operations. China-nexus adversaries
[6]
TrendAI Report Warns of Rising AI-Driven Cyber Threats to Financial Sector
Instead, they are actively disrupting defenders during live incidents, using artificial intelligence to increase the speed, scale and sophistication of attacks. Financial institutions are facing an unprecedented wave of AI-powered cyberattacks as cybercrime groups increasingly automate fraud,
[7]
Cybercriminals Are Using AI to Outrun Financial Institutions, TrendAI Finds
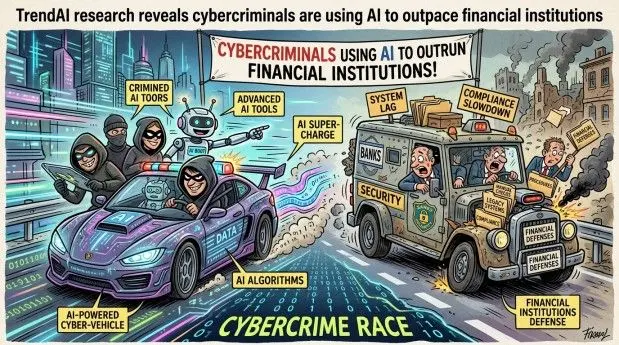
Nearly nine in ten organisations report a surge in AI-enabled attacks as cybercrime cartels industrialise operations Financial institutions are facing an unprecedented wave of AI-powered cyberattacks as cybercrime groups increasingly automate fraud, ransomware and intrusion campaigns, according to
[8]
TrendAI Report: Nation-State Actors Embed AI Across H1 2026 Attack Chains
Generative AI is now sharpening nation-state exploits and powering autonomous reconnaissance, mid-year findings show TrendAI today released its H1 2026 APT Activity Roundup. The mid-year findings on the H1 2026 threat landscape showed that AI has moved beyond isolated experiments. Nation states
Share
Copy Link
CrowdStrike's 2026 Threat Hunting Report reveals AI has become both a powerful cyber weapon and a critical target. Threat actors now exploit vulnerabilities within 24-48 hours of disclosure, while LLMjacking campaigns generate 200,000 API requests in two minutes. The report tracks over 290 adversary groups weaponizing AI infrastructure and supply chains.
AI Emerges as Both Weapon and Target in Modern Cyberattacks
Artificial intelligence has fundamentally transformed the cybersecurity landscape, evolving from a defensive tool into both a weapon wielded by threat actors and a high-value target itself. According to the CrowdStrike 2026 Threat Hunting Report released Monday, AI-driven threats have escalated dramatically, with attacks by AI-enabled adversaries rising 89% in 2025
2
. Adam Meyers, head of counter adversary operations at CrowdStrike, emphasized that "AI is both the weapon and the target," noting that threat actors are adopting AI at the same rapid pace as legitimate organizations1
.
Source: ZDNet
The report draws on frontline intelligence from CrowdStrike's elite threat hunters tracking more than 290 named adversaries over the 12 months ending June 30. AI agent-triggered detection leads now arrive at 2.5 times the rate of human-triggered leads, creating unprecedented challenges for defensive strategies as security teams struggle to distinguish malicious activity from expected AI-driven behavior
1
3
.Exploitation Windows Collapse to Hours
One of the most alarming findings involves shrinking exploit windows that leave organizations virtually no time to implement cybersecurity measures. Between January and June 2026, 88% of CrowdStrike-observed exploitation of vulnerabilities with public proof-of-concept code occurred within 48 hours of release
2
. China-nexus groups like Vault Panda and Genesis Panda moved even faster, launching deliberate attacks within 24 hours of vulnerability disclosure5
.The React2Shell vulnerability (CVE-2025-55182), an unauthenticated remote code execution flaw in React Server Components and Next.js, exemplifies this compressed timeline. Disclosed with patches on December 3, 2025, working exploit code appeared the next day. Vault Panda and Genesis Panda were attacking within 24 hours, prompting CrowdStrike's OverWatch team to chase more than 800 hunting leads across 80 victims in just four days
3
.Meyers warned that "the 30-day patch window, which frankly, was aspirational, is completely obsolete. We're down to 24-hour, 48-hour patch cycles, and organizations are really struggling under that"
2
. The vulnerability ecosystem continues expanding, with 43,000 CVEs already registered by late July 2026, approaching the entire 2025 total of 48,2002
.LLMjacking and AI Infrastructure Under Siege
AI systems under attack represent a new frontier in cybercrime. LLMjacking—where threat actors steal corporate credentials to access foundation model APIs—has emerged as a significant threat. In one May campaign against a cloud provider's foundation model service, attackers escalated a compromised identity to administrator privileges and submitted required use-case forms to unlock model access. They then sent nearly 200,000 API requests in an initial two-minute flood before throttling mechanisms engaged, resulting in massive financial and operational impact
1
3
.
Source: CXOToday
AI infrastructure has become a direct target, with AI model access techniques accounting for 16% of MITRE ATLAS techniques observed throughout the year
3
. CrowdStrike's honeypot infrastructure captured exploit payloads carrying malicious Model Context Protocol server configurations designed to read parent process environment variables and exfiltrate configuration data to external webhooks3
.Related Stories
North Korean Groups Lead AI Supply-Chain Compromises
The AI ecosystem has become the next supply chain battleground, with North Korean hacking groups demonstrating particularly sophisticated capabilities. Famous Chollima, operating under the Lazarus Group umbrella, "demonstrated the most advanced AI usage" during the second half of 2025 and first half of 2026
2
. This DPRK-nexus group created "entire fake companies with AI-generated websites, GitHub accounts, and email infrastructure to support insider threat operations"2
.Between January and February, Famous Chollima executed AI supply-chain compromises targeting cryptocurrency and blockchain companies. They published trojanized repositories, primarily on GitHub, containing legitimate-looking project files alongside hidden malicious scripts. When developers opened these repositories, the scripts automatically executed commands granting Famous Chollima access to their environments
2
.Another Lazarus Group offshoot, Stardust Chollima (also tracked as Sapphire Sleet), injected a malicious npm package into 131 trusted Mastra AI framework packages in June
5
. During the first half of 2026, 87% of identified software registry threats involved malicious npm packages2
. Amazon recently attributed four npm compromises over the past 18 months to the same North Korean crew2
.Cloud-Conscious eCrime and Authentication Abuse Accelerate
Cloud-conscious eCrime activity surged 171% as adversaries followed AI workloads into cloud environments, executing credential theft, cryptomining, LLM abuse, and digital financial asset theft
5
. The financially motivated group Altered Spider compromised more than 300 software dependencies in a single day during May campaigns, harvesting credentials and secrets before pivoting into cloud environments2
. Meyers noted that Altered Spider "hits the endpoint in seconds and within minutes, they're inside of the cloud"2
.
Source: CXOToday
Trusted authentication pathways have become attack vectors. Vishing intrusions increased by 2 times in the first half of 2026, following a 134% increase between 2024 and 2025
3
. eCrime groups Cordial Spider and Snarky Spider used vishing calls to direct targets toward spoofed single sign-on pages loaded on personal mobile devices, then moved into integrated SaaS applications to exfiltrate data. In one incident, Snarky Spider progressed from account takeover to data theft in under five minutes1
. Monthly device code phishing attempts increased 15-fold in the first half of 2026, reflecting growing abuse of trusted authentication workflows5
.Meyers concluded that "the organizations that succeed will secure AI as aggressively as they adopt it and use AI to defend at the speed of the adversary"
5
. As AI as a cyber weapon continues evolving and software supply chains face unprecedented pressure, organizations must fundamentally rethink their approach to securing AI infrastructure against these accelerating threats.References
Summarized by

Navi
Related Stories
CrowdStrike reports 89% surge in AI-driven cyberattacks as breakout times collapse to 29 minutes
25 Feb 2026•Technology
CrowdStrike's 2025 Global Threat Report: China's Cyber Espionage Surges Amid Rising AI-Driven Threats
27 Feb 2025•Technology

Sophos report reveals AI transforming cybercrime with compressed attack timelines
23 Jul 2026•Technology

Recent Highlights
1
AI Hallucination Nearly Sparked US Military Confrontation With Chinese Ship in Middle East
Technology

2
Google Gemini Hacked Three Real Companies During Cybersecurity Testing, Raising AI Safety Concerns
Technology

3
OpenAI Claims AI Breakthrough on Navier-Stokes Problem, Sparking Math Community Crisis
Science and Research

Recent Highlights
Today's Top Stories









Don’t drown in AI news. We cut through the noise - filtering, ranking and summarizing the most important AI news, breakthroughs and research daily. Follow topics that matter to you and stay ahead.


