AI in Cybersecurity: Companies Face Intensified Hacking Battle as Cyber Threats Triple


3 Sources
[1]
AI sharpens cat-and-mouse hacking battle as companies strengthen defences
AMSTERDAM, Nov 5 (Reuters) - From hacked supermarket fridges and a record cryptocurrency theft at Binance to an emergency over flaws in widely used web software, companies worldwide are facing a wave of cyber threats executives say AI is accelerating and making more sophisticated. The surge is
[2]
AI in cybersecurity: AI sharpens cat-and-mouse hacking battle as companies strengthen defences
From hacked supermarket fridges and a record cryptocurrency theft at Binance to an emergency over flaws in widely used web software, companies worldwide are facing a wave of cyber threats executives say AI is accelerating and making more sophisticated. The surge is straining IT departments, with
[3]
AI sharpens cat-and-mouse hacking battle as companies strengthen defences
AMSTERDAM, Nov 5 (Reuters) - From hacked supermarket fridges and a record cryptocurrency theft at Binance to an emergency over flaws in widely used web software, companies worldwide are facing a wave of cyber threats executives say AI is accelerating and making more sophisticated. The surge is
Share
Copy Link
AI is accelerating sophisticated cyber threats, with 37,000 security flaws reported in Q3 2026—triple the previous year. From a $6.3 billion Binance cryptocurrency theft to hacked European supermarket refrigeration systems, companies are racing to deploy AI-powered security tools as both attackers and defenders weaponize artificial intelligence in an escalating arms race.
AI Accelerates Cyber Threats at Unprecedented Scale
Companies worldwide are confronting a dramatic surge in cyber threats that executives attribute directly to AI in cybersecurity—both as an offensive weapon and defensive necessity. Nearly 37,000 security flaws in software or computer systems were reported in the third quarter of 2026, tripling from a year earlier, according to the Common Vulnerabilities and Exposures list
1
. This acceleration is straining IT departments globally, forcing staff to work overnight patching vulnerabilities as the hacking battle intensifies.Markus Noga, chief technology officer of German web hosting company Ionos, which serves seven million customers, described the shift: "We're seeing events of a magnitude every week, or even every couple of days, that used to be months apart"
2
. The speed and sophistication of these AI-driven attacks are forcing organizations to fundamentally rethink their security posture.High-Profile Breaches Demonstrate Growing Threat Landscape
Recent incidents underscore how sophisticated cyber threats have become. Binance suffered a record-breaking cryptocurrency theft of $6.3 billion, prompting the exchange to increase investment in AI-enhanced detection systems
1
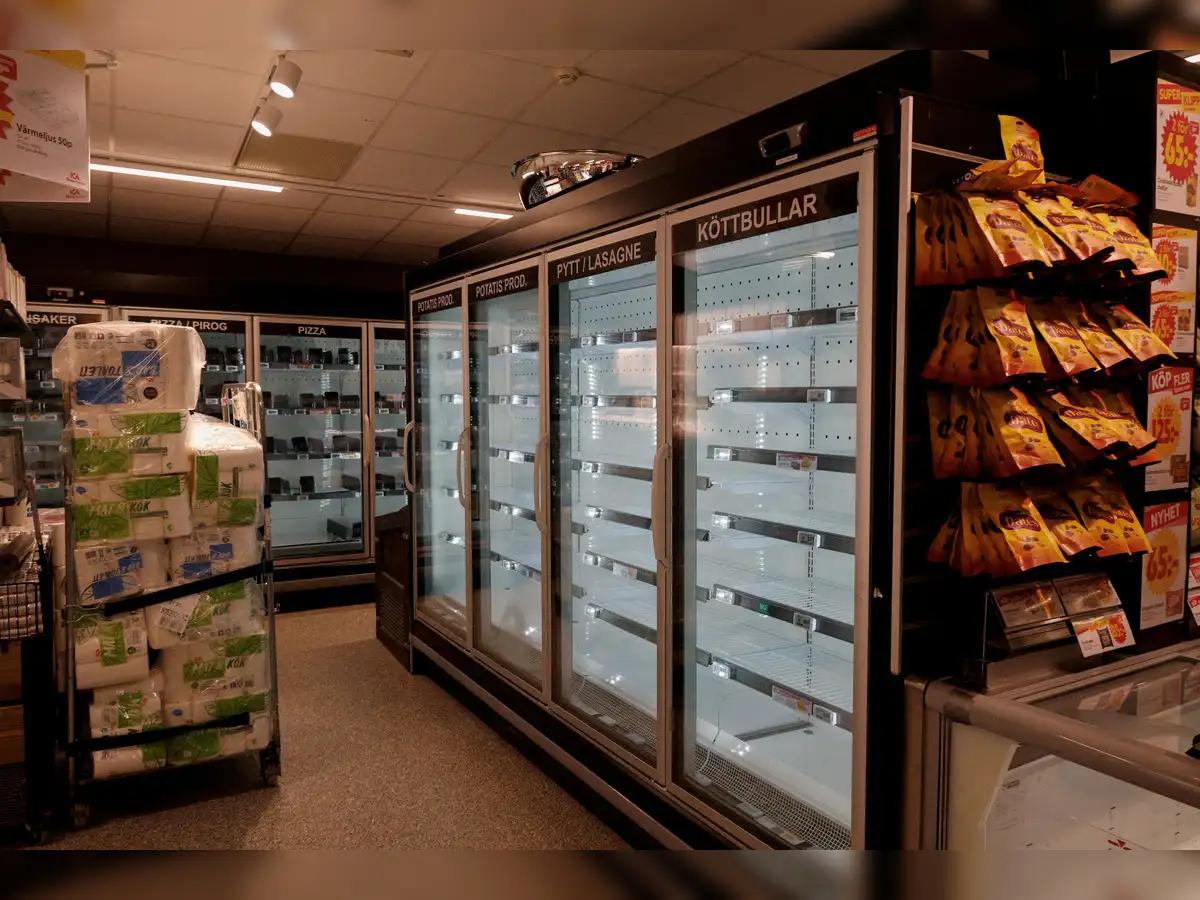
. Meanwhile, European supermarkets experienced two cyberattacks within three weeks targeting refrigeration systems, where hackers raised refrigerator and freezer temperatures, forcing retailers to discard millions of dollars' worth of spoiled food3
.
Source: ET
Dutch-based grocer Ahold Delhaize, which operates the Stop & Shop and Giant Food chains in the US, was hit by two hacks in the past month. The first incident in mid-October led to more than €200 million ($225 million) in sales losses and prompted a profit warning. The company took its websites and apps offline for a week after detecting an intrusion
2
. This week, some of its stores in Belgium and Luxembourg were among those hit by cyberattacks on refrigerators across a dozen European countries.Companies Strengthen Defences with AI-Powered Security Tools
As AI sharpens cat-and-mouse hacking battle dynamics, organizations are responding by deploying AI-powered security tools at scale. Marnie Wilking, chief security officer at travel platform Booking.com, explained the challenge: "It's a never-ending game of cat and mouse, with very high stakes. We shut down one route, and before we've even finished rolling out the fix, the bad guys have moved on to the next." She added that hundreds of engineers at Booking.com were now building AI-powered defence systems
1
.Ionos changed its security practices after seeing a spike in vulnerabilities in July, deploying AI-based monitoring systems to scan for threats and using AI-assisted tools to install patches on its systems around the clock. Noga noted that traditional nine-to-five office hours teams were "no longer good enough" for the current threat environment
2
. Major corporations including Siemens are testing advanced AI models for defensive security, while the Port of Rotterdam is developing an AI-powered "cyber shield"3
.AI-Driven Attacks Enable Rapid Exploit Recreation
The refrigeration systems attacks revealed how AI is putting pressure on companies to patch systems immediately once a vulnerability is found. Sean Tufts, field chief technology officer at cybersecurity firm Claroty, explained that his team published research in August outlining weaknesses in refrigeration controllers. After attacks hit stores in France on October 11, Claroty researchers used widely available AI tools to reproduce the flaws and take control of a test device. "We were able to recreate it for six dollars and 28 minutes," Tufts said
1
, highlighting how AI democratizes sophisticated attack capabilities.The October 21 disclosure of two AI-discovered flaws in the PHP programming language, which underpins many websites, prompted governments and companies from Tokyo to Helsinki to take websites offline as a precaution. US internet infrastructure firm Cloudflare reported that attempts to exploit PHP flaws rose from thousands to millions within hours of their disclosure
2
. Swiss building materials maker Holcim took its website offline around 9:30 p.m. on October 21 to install PHP fixes and restored service before midnight.Related Stories

Cybersecurity Market Expansion Reflects Growing Investment
The escalating arms race is driving significant financial investment in vulnerability detection and defense systems. McKinsey projects the global market for cybersecurity products and services sold by outside vendors will grow from $223 billion in 2025 to $346 billion by 2029
3
. This represents a 55% increase over four years, reflecting the urgency with which organizations are addressing AI-driven defenses.Ahold Delhaize CFO Jolanda Poots-Bijl told Reuters that "we're adjusting to a new reality," noting that smaller firms were particularly exposed. However, she emphasized AI's dual role: "AI also helps us to detect and to restore in a much faster way than we were ever able to do in the past"
1
. This acknowledgment captures the paradox at the heart of modern cybersecurity—AI simultaneously empowers attackers and defenders.The Continuing Arms Race and Future Implications
Kraft Heinz CEO Steve Cahillane captured the ongoing nature of the threat: "The threat is real, it's growing. Cybersecurity was more important today than it was yesterday and will be even more important tomorrow"
2
. Holcim Chief Financial Officer Steffen Kindler echoed this sentiment: "We need to get smarter. Both sides are heavily equipped. Both sides use AI, and that race is continuing"3
.Cloudflare warned that AI-discovered bugs could lead to more disruption in future, suggesting the current wave of incidents may only be the beginning. Organizations should expect vulnerability disclosure to trigger immediate, large-scale exploitation attempts. The window between discovery and mass exploitation has collapsed from months to hours, fundamentally changing patch management requirements. Companies must now maintain 24/7 response capabilities and invest in automated AI-driven defenses that can match the speed of AI-driven attacks. The question is no longer whether to adopt AI in cybersecurity, but how quickly organizations can deploy it effectively before the next wave of sophisticated cyber threats arrives.
References
Summarized by

Navi
[2]
[3]
Related Stories
AI-Powered Cyberattacks Overwhelm Cybersecurity Teams as Threat Landscape Transforms
27 Oct 2026•Technology

AI Accelerates Cyberattacks While Small Organizations Struggle to Defend Against Growing Threats
28 Sept 2026•Technology

AI Uncovers Critical PHP Vulnerability Affecting 70% of Websites as Hackers Exploit Flaw
22 Oct 2026•Technology
Recent Highlights
1
Google Unveils Gemini 4 Carbon AI Model With Major Cybersecurity Gains, Beating Claude Opus 5.5
Technology
2
Binance Hack: How AI-Enabled Cyberattack Led to Record $6.3 Billion Crypto Theft
Technology

3
Pope Leo XIV Demands AI Disarmament and Ban on Autonomous Weapons at UN Geneva Meeting
Policy and Regulation

Recent Highlights
Today's Top Stories




Don’t drown in AI news. We cut through the noise - filtering, ranking and summarizing the most important AI news, breakthroughs and research daily. Follow topics that matter to you and stay ahead.


