Artemis Raises $70M to Fight AI-Powered Attacks With AI-Native Security Platform


4 Sources
[1]
Artemis raises $70M to help fight AI-powered attacks with AI | Fortune
Felicis led the Series A with returning investors First Round Capital and Brightmind. The round was also joined by Theory VC and prominent cybersecurity industry leaders, including founders of Demisto and Abnormal AI, the former CEO and CTO of Splunk, and senior executives from CrowdStrike, Palo
[2]
Artemis reels in $70M to make breach remediation more efficent with AI - SiliconANGLE
Artemis reels in $70M to make breach remediation more efficent with AI Six-month-old cybersecurity startup Artemis Global Technologies Inc. today disclosed that it has raised $70 million in funding. The capital arrived in two tranches. Felicis led the largest of the two transactions, a Series A
[3]
Artemis Emerges from Stealth with $70M to Rebuild Security Operations for AI-Powered Attacks
New platform from former Abnormal AI, AWS, and Palo Alto Networks leaders replaces static detection with adaptive, AI-native defense to combat autonomous threats at enterprise scale. NEW YORK, April 15, 2026 (Newswire.com) - Artemis, an AI-native protection platform that delivers real-time
[4]
Artemis Raises $70 Million to Counter AI-Powered Cyberthreats With AI | PYMNTS.com
By completing this form, you agree to receive marketing communications from PYMNTS and to the sharing of your information with our sponsor, if applicable, in accordance with our Privacy Policy and Terms and Conditions. That's according to a Wednesday (April 15) report from Fortune, which described
Share
Copy Link
Six-month-old cybersecurity startup Artemis emerged from stealth with $70 million in combined seed and Series A funding to combat AI-powered attacks that move at machine speed. Founded by former AWS and Abnormal Security leaders, the company offers an AI-native protection platform that replaces traditional rule-based systems with adaptive, automated threat response.
Artemis Secures $70M in Cybersecurity Funding to Combat Machine Speed Attacks
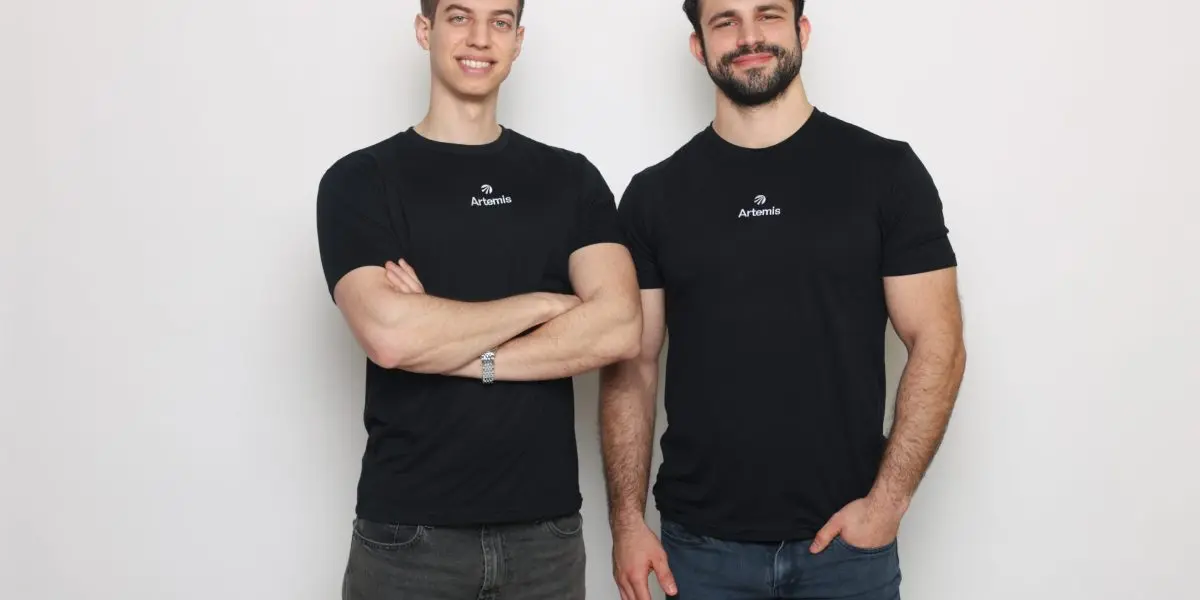
Artemis Global Technologies emerged from stealth with $70 million in combined seed and Series A funding, just six months after its founding by CEO Shachar Hirshberg, a former AWS product leader, and CTO Dan Shiebler, previously head of AI at Abnormal Security
1
. Felicis led the Series A funding round with participation from returning investors First Round Capital and Brightmind, alongside Theory VC and prominent cybersecurity industry leaders including founders of Demisto and Abnormal AI, the former CEO and CTO of Splunk, and senior executives from CrowdStrike, Palo Alto Networks, Microsoft, and Okta1
.
Source: Fortune
The company expects to achieve multi-million dollars in ARR before the end of 2026, having already closed several seven-figure deals with clients including Mercury, Wix, Lemonade, and Abnormal AI
1
. This rapid traction reflects the urgent need for security operations platforms that can match the speed of AI-powered attacks, which now unfold in minutes rather than hours or days.AI-Powered Attacks Demand New Approach to Security Operations
Traditional security tools struggle to keep pace with attackers who now leverage AI to execute attacks at machine speed, sometimes completing intrusions within minutes
1
. A March report from CrowdStrike highlighted that the time to attack has dropped dramatically, while Anthropic's recent Mythos preview demonstrates how AI can identify vulnerabilities faster than most organizations can patch them1
.
Source: PYMNTS
"It was clear to us that the traditional architectures and products weren't cut out to what companies need in the age of AI," said Hirshberg
1
. Most companies still rely on rigid, rule-based systems and disconnected tools, leaving security teams to piece together what happened only after damage is done. Once attackers gain access, they can automate large parts of the attack chain, reducing the time defenders have to respond and demanding a completely different approach to security1
.Shiebler noted that AI enables less sophisticated attackers to launch more sophisticated attacks, raising the bar on what defenders need to do in general
1
. "This isn't just about the future getting worse," Hirshberg emphasized. "The capabilities that exist today are already incredibly powerful, and attackers are leveraging them right now"4
.AI-Native Protection Platform Offers SIEM Alternative
Artemis positions its platform as a next-generation alternative to traditional SIEM platforms like Splunk, which Cisco acquired in 2024 for $28 billion
1
. The company's AI-native protection approach constantly monitors everything happening across a company—logins, cloud activity, applications—learning what "normal" looks like for that specific organization and instantly spotting anomalies1
.At the core of Artemis is a proprietary dynamic data model built from each customer's own telemetry, fusing behavioral log data across users, machines, cloud workloads, and applications with business context to understand whether an action makes sense for that specific organization
3
. "At the core of Artemis is a data model I've been iterating on for years," said Shiebler. "The real breakthrough isn't just using better AI models, but in giving those models deep, structured understanding of how an organization functions, making reliable detection and automated response possible"3
.The platform addresses traditional SIEM cost challenges through federated querying, which analyzes cybersecurity telemetry in the system where it's generated rather than requiring data ingestion
2
. This approach provides full visibility at a fifth of the cost of traditional architectures that penalize visibility through linear scaling with data volume3
.Related Stories
Automated Threat Response and Breach Remediation at Machine Speed
Instead of flooding security teams with disconnected alerts, Artemis connects the dots into coherent attack stories and can automatically shut down threats—like locking a hacked account—before they spread
1
. The platform uses AI to automatically generate detectors and modify them when the threat landscape changes, scanning data from cloud environments, employee endpoints, and other systems2
.When Artemis finds a breach, it generates a visual timeline of how the cyberattack unfolded alongside a natural language incident description containing technical details
2
. For example, if a privilege escalation in Okta coincides with unusual API activity in AWS, Artemis contextualizes both signals and surfaces a single correlated narrative rather than two disconnected alerts, eliminating manual investigation3
.Administrators can query additional breach data through a chat interface, and the platform generates remediation suggestions such as blocking IP addresses or rotating compromised passwords
2
. "Agentic threat hunting proactively looks for suspicious activities," Hirshberg explained. "Every security signal triggers an autonomous investigation that understands your baseline. You get a full story: here's what happened, here's the context, here's the evidence, here's what can be contained, here's what needs your judgment"2
.Early Traction Demonstrates Enterprise-Scale Impact
In less than six months since company formation, Artemis is deployed in production and processing billions of events per hour for enterprise customers in technology, banking, and financial services
3
. At one technology company with thousands of employees, Artemis's first scan surfaced multimillion-dollar cloud spend savings and shadow activity invisible to existing tools, including over-privileged accounts, undocumented integrations, and workflows calling APIs with elevated privileges3
.Another early customer, a highly regulated company with tens of thousands of employees, now completes investigations in under five minutes—a 96% reduction in time to resolution
3
. The company works closely with advanced frontier AI labs and models, ensuring it stays at the cutting edge of how both attackers and defenders operate3
.Felicis partner Jake Storm pointed to a long-standing cycle in cybersecurity between bundling and unbundling tools, arguing that AI is pushing the industry back toward a centralized "brain" for security operations—one system that ingests data, reasons across it, and acts in real time
1
. This represents a major shift from today's fragmented landscape, though the company enters a crowded space where nearly every major security vendor races to integrate AI while startups proliferate with similar claims about autonomous detection. Storm insisted that Artemis is positioned to succeed because it's built for a fundamentally different threat landscape where attacks are cheap, constant, and automated, and where traditional, human-driven security workflows no longer suffice1
.References
Summarized by

Navi
[2]
[3]
Related Stories
7AI raises $130M Series A to automate cybersecurity investigations with AI agents
05 Dec 2025•Startups

Corma Raises $60M to Build Defensive AI as Tests Show Attackers Win 88% of Simulations
10 Aug 2026•Technology

AIR Security Emerges With $50M to Build First Firewall for AI Agents Across Enterprise Systems
01 Sept 2026•Technology
Recent Highlights


Recent Highlights
Today's Top Stories








Don’t drown in AI news. We cut through the noise - filtering, ranking and summarizing the most important AI news, breakthroughs and research daily. Follow topics that matter to you and stay ahead.


