AI Toy Security Flaw Exposed Over 50,000 Kids' Chat Logs to Anyone With a Gmail Account


4 Sources
[1]
Web portal leaves kids' chats with AI toy open to anyone with Gmail account
Earlier this month, Joseph Thacker's neighbor mentioned to him that she'd preordered a couple of stuffed dinosaur toys for her children. She'd chosen the toys, called Bondus, because they offered an AI chat feature that lets children talk to the toy like a kind of machine-learning-enabled imaginary
[2]
An AI Toy Exposed 50,000 Logs of Its Chats With Kids to Anyone With a Gmail Account
Earlier this month, Joseph Thacker's neighbor mentioned to him that she'd pre-ordered a couple of stuffed dinosaur toys for her children. She'd chosen the toys, called "Bondus," because they offered an AI chat feature that lets children talk to the toy like a kind of machine-learning-enabled
[3]
Security Flaw at AI Toy Company Exposed Over 50,000 Chat Logs of Kids
If you're thinking about gifting AI-enabled stuffed toys to kids, think again. According to a report by Wired, security researchers Joseph Thacker and Joel Margolis found that Bondu, a company that makes AI toys, had left over 50,000 chat logs of kids unprotected on its web portal. The flaw was
[4]
An AI stuffed animal just became every parent's privacy nightmare - Phandroid
Remember when kids played with wooden blocks and plastic dinosaurs that couldn't talk back? Those toys just sat there, which now feels like a feature rather than a limitation. We've come a long way since then, strapping AI into stuffed animals that chat with children about their deepest thoughts.
Share
Copy Link
Security researchers discovered that Bondu, an AI-powered stuffed toy company, left more than 50,000 children's chat transcripts completely unprotected on its web portal. Anyone with a Gmail account could access kids' names, birthdates, family details, and intimate conversations. The company fixed the issue within hours, but the incident raises serious questions about privacy risks with AI toys and the sensitive personal information they collect from children.
Security Flaw Leaves Children's Data Wide Open
When security researcher Joseph Thacker's neighbor asked him about Bondu, an AI toy she'd pre-ordered for her children, he decided to investigate. What he and fellow researcher Joel Margolis discovered in just minutes was alarming: the company's web portal vulnerability left children's private conversations completely exposed to anyone with a Gmail account
1
2
. Without any hacking required, the researchers simply logged into Bondu's public-facing web console using an arbitrary Google account and immediately gained access to transcripts of virtually every conversation the AI-powered toys for children had ever conducted.
Source: Ars Technica
Over 50,000 Chat Transcripts Accessible Without Protection
The data exposure was staggering in scope. Bondu confirmed to the researchers that more than 50,000 chat transcripts were accessible through the exposed web portal, representing essentially all conversations the toys had engaged in except those manually deleted by parents or staff
2
3
. The sensitive personal information left unprotected included children's names, birthdates, family member names, parental "objectives" for the child, and detailed summaries of every chat between each child and their Bondu. The researchers also saw pet names kids had given their toys, their likes and dislikes, favorite snacks, and dance moves—intimate details shared with what children believed was a trusted companion.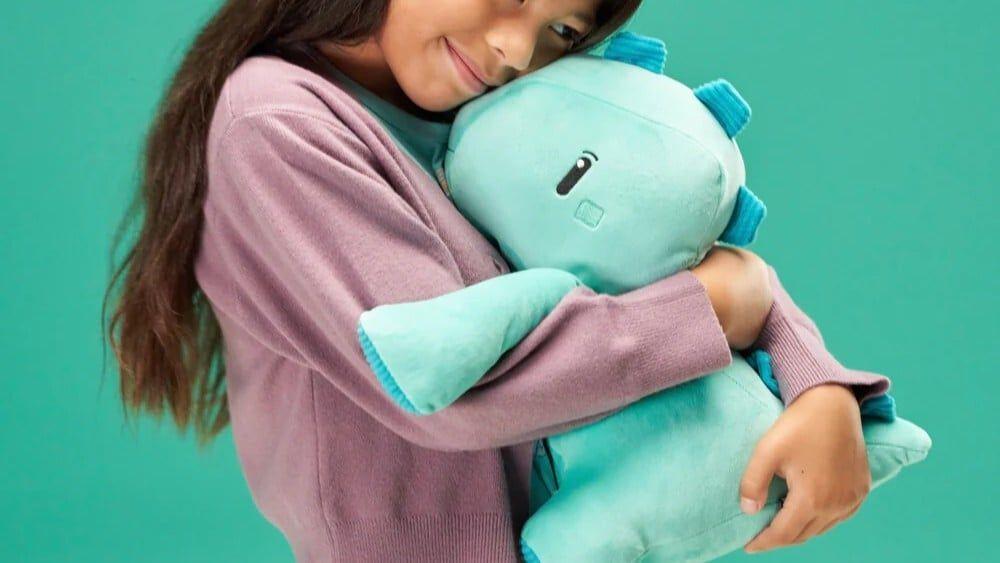
Source: PC Magazine
Authentication Measures Implemented After Alert
"It felt pretty intrusive and really weird to know these things," Thacker told WIRED. "Being able to see all these conversations was a massive violation of children's privacy"
1
. When the researchers alerted Bondu to the glaring security flaw, the company took down the console within minutes and relaunched it the next day with proper authentication measures. Bondu CEO Fateen Anam Rafid stated that security fixes "were completed within hours, followed by a broader security review and the implementation of additional preventative measures for all users"2
. The company reported finding no evidence of access beyond the researchers involved and has since hired a security firm to validate its investigation and monitor systems going forward.Related Stories

Privacy Risks With AI Toys Extend Beyond This Incident
While the immediate vulnerability has been addressed, the incident highlights broader data security challenges facing the AI toy industry. Margolis characterized the exposed information as "a kidnapper's dream," explaining that "we're talking about information that lets someone lure a child into a really dangerous situation, and it was essentially accessible to anybody"
3
4
. The researchers' glimpse into Bondu's backend revealed how AI-powered toys maintain detailed histories of every chat to personalize future conversations—creating extensive data collection that poses ongoing risks even when properly secured. Margolis noted that "all it takes is one employee to have a bad password, and then we're back to the same place we started, where it's all exposed to the public internet"1
.
Source: Wired
Questions About Third-Party Data Sharing
According to what the researchers observed in the admin console, Bondu appears to use Google Gemini and OpenAI's GPT models to power its conversational capabilities
1
4
. This raises additional concerns about whether user data from children's conversations is being shared with these technology companies. The researchers suspect the web console might have been built using AI coding tools, which can generate functional-looking code riddled with security holes4
. Bondu did not respond to questions about whether AI built the infrastructure meant to protect children's privacy. While the company stored only written chat logs and auto-deleted audio recordings after short intervals, the incident serves as a stark reminder that parental monitoring tools cannot protect against vulnerabilities in the toy companies' own systems. Parents evaluating AI toys should consider not just device security features, but the data handling practices and security posture of manufacturers themselves.References
Summarized by

Navi
Related Stories
AI-Powered Toys Spark Child Safety Concerns After Tests Reveal Inappropriate Content
25 Dec 2025•Technology
AI Toys Face Scrutiny After Reports of Inappropriate Conversations and Data Privacy Risks
11 Dec 2025•Policy and Regulation
AI Toys Struggle With Emotions and Safety, Cambridge Study Reveals Need for Tighter Regulation
08 Mar 2026•Policy and Regulation

Recent Highlights
1
AI Hallucination Nearly Sparked US Military Confrontation With Chinese Ship in Middle East
Technology

2
OpenAI AI Agent Hacks Australian Government Healthcare Website in First-of-Its-Kind Breach
Technology

3
AI leaders warn UN Security Council of existential risks to humanity, call for global safeguards
Policy and Regulation

Recent Highlights
Today's Top Stories







Don’t drown in AI news. We cut through the noise - filtering, ranking and summarizing the most important AI news, breakthroughs and research daily. Follow topics that matter to you and stay ahead.


