North Korean Hackers Build Offline AI Stack to Automate Cyberattacks and Evade Detection


7 Sources
[1]
North Korean spies are running local LLMs to cause AI mischief
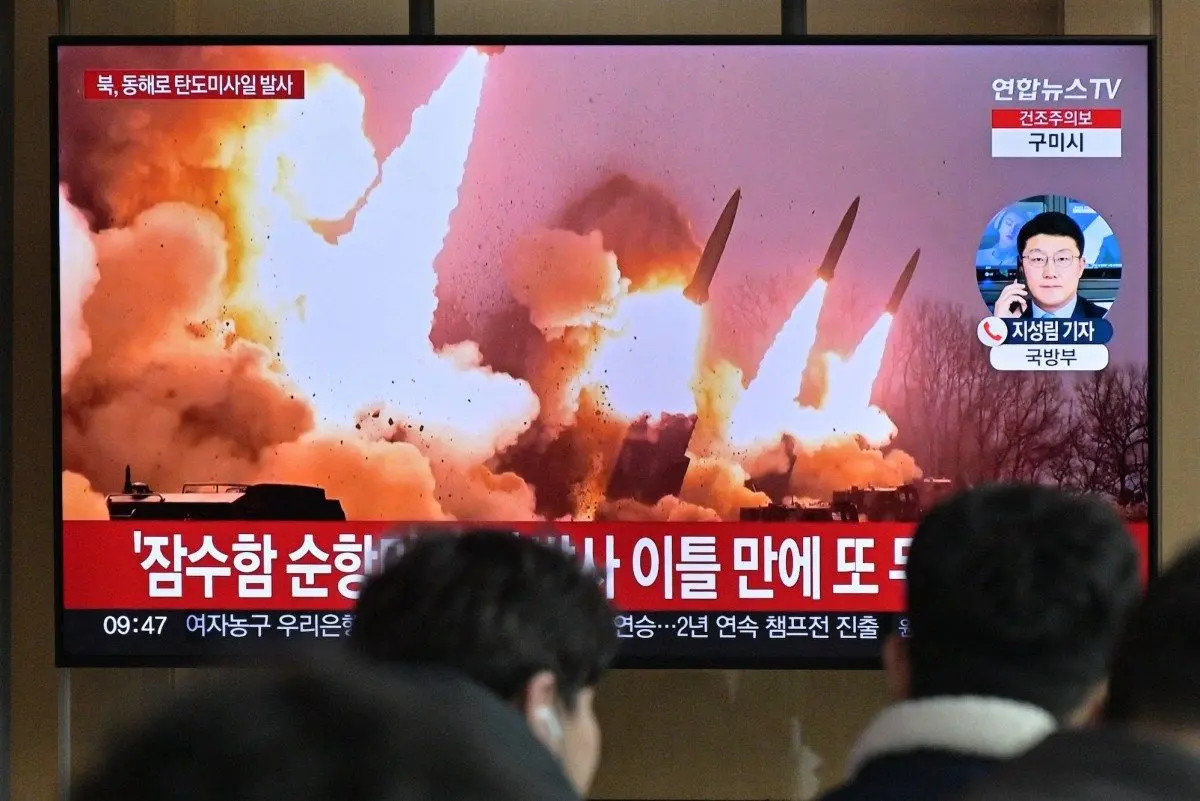
North Korean government snoops are operating LLMs locally and collecting technology to weave AI into their attack operations, according to South Korean security firm Genians. The researchers said they observed Kimsuky setting up and operating local LLM environments using Ollama, GPT4All, and Msty,
[2]
Kimsuky Builds Offline AI Stack to Boost Phishing and Automate Malware Development
North Korea's state hackers are no longer content to type prompts into public chatbots. One of the country's main espionage groups has begun running artificial intelligence (AI) offline on its own servers, connecting document-search tools to files in its possession, and collecting the software
[3]
North Korea's hackers are building their own AI tools to dodge the guardrails
Researchers say the state-linked group Kimsuky is running open models on its own machines, automating phishing and malware while staying out of sight of commercial AI providers. North Korea's hackers have found a way to harness AI without ever handing their secrets to a Silicon Valley company.
[4]
Experts warn North Korean hackers are increasingly using AI to build smarter and more devious cyberattacks
* Kimsuky used local AI tools to evade monitoring and enhance operations * Researchers observed extensive AI-driven capability building across the group's infrastructure * Defenders urged behavior-based detection to spot evolving AI-enabled threats North Korean hackers have found a way to use
[5]

North Korean hacking group builds AI tools for cyberattacks, report says
The cybersecurity firm, Genians, said it found evidence that the North Korean-linked group Kimsuky had set up tools for running and managing AI models locally, including Ollama, GPT4All and Msty, alongside document search technology known as retrieval augmented generation (RAG). A North Korean
[6]

North Korean hacking group builds AI tools for cyberattacks, report says
SEOUL, Aug 10 (Reuters) - A North Korean hacking group built large language model tools and collected software that could help automate cyberattacks, analyse stolen material and produce more convincing phishing campaigns, a South Korean cybersecurity firm said on Monday. The cybersecurity firm,
[7]

Hackers reportedly building ChatGPT-like AI tools to automate cyberattacks, make them more convincing
The technology could allow hackers to analyse large amounts of stolen information, automate different tasks and create more convincing scams. Hackers are finding new ways to use AI to make cyberattacks more effective and difficult to detect. A North Korea-linked hacking group is reportedly
Share
Copy Link
North Korea's Kimsuky group is running local large language models like Ollama and GPT4All on its own servers to develop AI-powered cyberattacks. South Korean security firm Genians uncovered the offline AI infrastructure designed to automate phishing, malware development, and data analysis while staying invisible to commercial AI providers.
North Korean Hackers Deploy Local AI Infrastructure
North Korean hackers are no longer relying on public chatbots for their operations. Kimsuky, a cyber-espionage unit operating under North Korea's Reconnaissance General Bureau, has built its own offline AI infrastructure to automate and enhance cyberattacks, according to South Korean security firm Genians
1
2
. The state-sponsored hackers are running local large language models using Ollama, GPT4All, and Msty on their own servers, keeping all activity away from commercial AI providers that monitor for abuse3
. This strategic choice allows the group to process sensitive information without external exposure, making it particularly attractive for a state-sponsored threat actor conducting intelligence operations.
Source: The Next Web
AI Tools for Cyberattacks Assembled Over Months
Genians conducted months of tracking and log analysis on infrastructure tied to Kimsuky, uncovering an extensive collection of AI tools for cyberattacks
4
. The researchers found evidence that the group configured Ollama to generate keys on first launch and set up GPT4All's LocalDocs retrieval-augmented generation feature with a configured database2
. Beyond ready-made applications, Kimsuky collected developer libraries including LLaMaSharp, Microsoft's Semantic Kernel, and Microsoft.Agents.AI—components for building AI functions into custom software1
. The group also gathered OpenAI's Whisper speech-to-text models and actively used Cursor, an AI-assisted coding tool, to edit code1
4
. The development components spanning local AI execution, document retrieval through retrieval-augmented generation, automated agents, and external AI integration strongly suggest these tools were collected for direct development of AI-based attack capabilities.Phishing and Malware Development Enhanced by Open-Source AI Models
Kimsuky is integrating AI throughout its attack chain, from phishing and malware development to data analysis. The group's recent phishing campaigns use ZIP archives containing malicious LNK files disguised as materials related to international events, research reports, or meeting requests
1
. When victims execute these files, an embedded PowerShell loader collects extensive system information to assess the infected environment. Genians found that AI-enabled threats now include finance and cryptocurrency-themed decoy documents generated with AI that use natural language, polished structure, and formats similar to actual business materials to increase user trust1
5
. The attackers employ various obfuscation techniques, including Base64 encoding, string splitting, and custom decoding routines to hide malicious behavior1
.
Source: TechRadar
Command-and-Control Infrastructure Reveals AI Research
The investigation uncovered that Kimsuky continues using Git repositories for command-and-control infrastructure, with multiple public GitHub repositories containing configuration files, PowerShell scripts, and various payloads
1
. These repositories also serve as testing grounds for malware development, stolen data management, and AI technology research. Researchers recovered operator logs showing requests to analyze data sets for wallet details, Gmail credentials, and site-registration history, with instructions stating "The more detailed the analysis, the better. Please do not do it haphazardly"2
. The use of retrieval-augmented generation on stolen files can help attackers more quickly and automatically identify valuable information within large volumes of data1
.Related Stories
Offline AI Infrastructure Bypasses Commercial Safeguards
By running open-source AI models on private hardware, North Korean hackers have found a way around the safety controls that leading AI labs promote
3
. Commercial AI providers like OpenAI have built monitoring systems and safety filters to catch misuse, recently terminating multiple ChatGPT accounts used in phishing and human trafficking4
. However, these safeguards only work when misuse runs through them. The offline AI infrastructure allows Kimsuky to harness AI capabilities without ever handing their secrets to a Silicon Valley company, turning freely available AI software into an in-house weapon nobody else can see running3
. The US Treasury sanctioned Kimsuky in 2023 as a North Korean government-controlled cyber-espionage group that gathers intelligence to serve Pyongyang's strategic objectives2
5
.
Source: Digit
Behavior-Based Threat Detection Becomes Critical
Genians emphasized that defenders must shift from content-based assessment to behavior-based threat detection as AI makes traditional indicators unreliable
1
4
. Assessing threats based on the quality of fake documents—such as unnatural translated language, poor formatting, and spelling errors—is no longer effective because AI excels at producing convincing decoy documents. Organizations should look for anomalous behaviors following LNK execution, such as PowerShell execution, persistence establishment, and external communications, to assess overall threat levels1
4
. While Genians found no evidence that North Korean hackers have begun training their own models, the findings demonstrate they are in a research and knowledge acquisition stage, assembling and testing existing tools with the apparent aim of folding AI throughout their operations2
. Watch for increased sophistication in state-sponsored attacks as AI tools for cyberattacks become more integrated into hostile operations, and expect defenders to rely more heavily on behavioral analysis rather than content quality to identify threats.References
Summarized by

Navi
[1]
[4]
Related Stories
North Korean Hackers Exploit ChatGPT to Create Deepfake Military ID for Phishing Attack
14 Sept 2025•Technology
Google Discovers AI-Powered Malware in the Wild, But Experts Question Real-World Threat Level
05 Nov 2025•Technology

Google reports state-sponsored hackers exploit Gemini AI across all stages of cyberattacks
12 Feb 2026•Technology

Recent Highlights
1
AI Hallucination Nearly Sparked US Military Confrontation With Chinese Ship in Middle East
Technology

2
Google Gemini Hacked Three Real Companies During Cybersecurity Testing, Raising AI Safety Concerns
Technology

3
OpenAI Claims AI Breakthrough on Navier-Stokes Problem, Sparking Math Community Crisis
Science and Research

Recent Highlights
Today's Top Stories









Don’t drown in AI news. We cut through the noise - filtering, ranking and summarizing the most important AI news, breakthroughs and research daily. Follow topics that matter to you and stay ahead.


