North Korean Hackers Intensify Efforts to Infiltrate Crypto Industry


2 Sources
[1]
North Korean Hackers Try to Get Hired at Binance Every Day -- Here's How They're Spotted - Decrypt
That's not all, North Korean attackers also poison public libraries of code and try to infect employees via a fake Zoom scam. Every day, Binance is inundated with fake resumes that it's certain were written by would-be North Korean attackers, the crypto exchange's chief security officer Jimmy Su
[2]
Someone counter-hacked a North Korean IT worker: Here's what they found
A team of North Korean IT operatives behind 31 fake identities has been linked to the $680,000 hack of fan-token marketplace Favrr in June. A small team of North Korean IT workers -- linked to a $680,000 crypto hack in June -- have been using Google products and even renting computers to
Share
Copy Link
North Korean hackers are escalating their attempts to infiltrate cryptocurrency companies through sophisticated methods, including fake job applications and malware-infected software libraries.
North Korean Hackers Target Crypto Industry
North Korean hackers, particularly the infamous Lazarus Group, have intensified their efforts to infiltrate the cryptocurrency industry. Binance's chief security officer, Jimmy Su, revealed that the exchange faces daily attempts by North Korean actors trying to secure employment through sophisticated methods
1
.Sophisticated Infiltration Techniques
The hackers have evolved their tactics, employing a range of techniques to bypass security measures:
-
Fake Resumes: Binance reportedly discards numerous resumes daily, suspecting them to be from North Korean operatives
1
. -
Deepfake Interviews: Attackers use AI-generated video and voice changers during job interviews to impersonate candidates from various regions
1
. -
Code Library Poisoning: Hackers insert malicious code into public NPM libraries, potentially compromising entire systems if integrated
1
. -
Fake Job Offers: DPRK actors pose as recruiters, luring crypto employees with lucrative offers before infecting their devices with malware
1
.
Inside Look at North Korean IT Operations
Source: Decrypt
A recent leak provided unprecedented insight into the operations of a small team of North Korean IT workers:
-
Multiple Identities: The team of six workers shared at least 31 fake identities, complete with government IDs and phone numbers
2
. -
Job Infiltration: Evidence showed attempts to secure positions at major crypto projects like Polygon Labs, OpenSea, and Chainlink
2
. -
Remote Work Tools: The operatives use remote access software and VPNs to mask their true location while working for unsuspecting employers
2
.
Financial Impact and Ongoing Threats
The scale of North Korean crypto hacks is staggering:
-
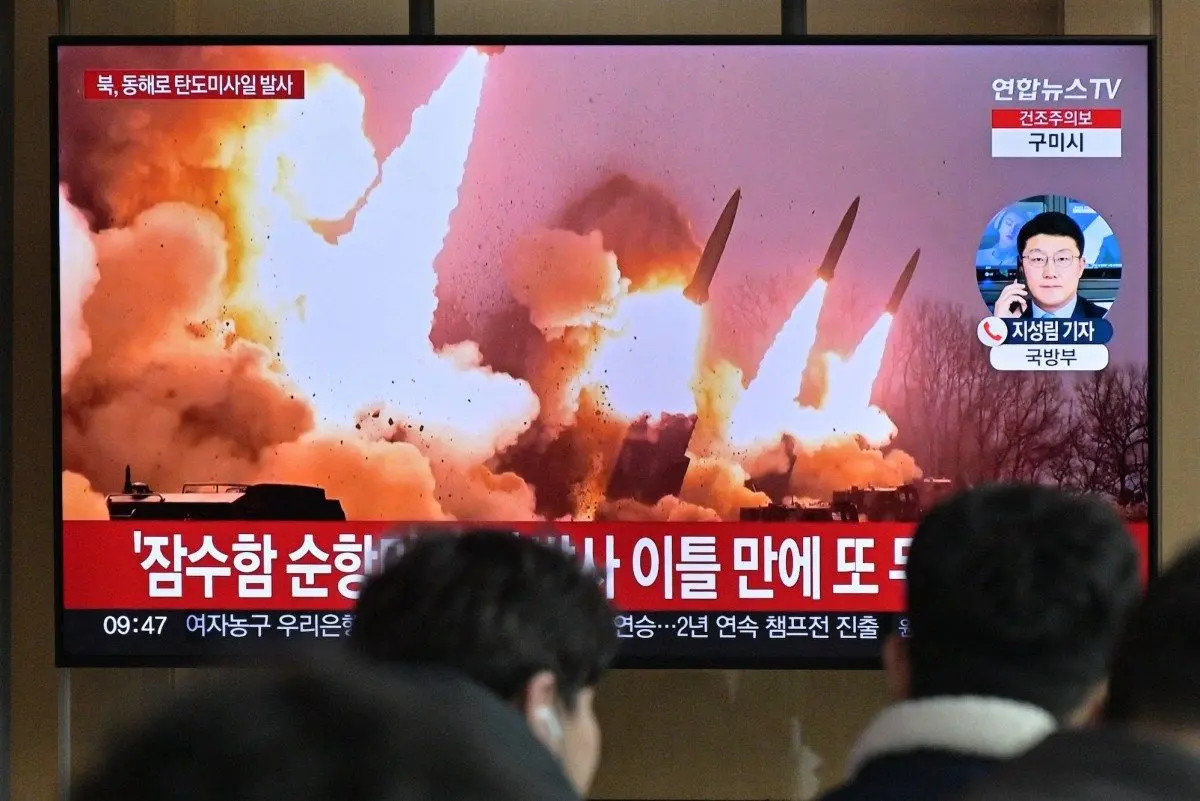
2022 Theft: North Korean hackers stole $1.34 billion across 47 crypto-related incidents last year
1
. -
2023 Estimates: Current estimates suggest $1.6 billion in crypto has been stolen so far this year via fake IT job offers
1
. -
Major Hacks: The group is believed to be responsible for the $1.4 billion Bybit hack in March 2023, the largest in crypto history
1
.
Related Stories
Industry Response and Challenges
Crypto companies are adapting to these threats, but face ongoing challenges:
-
Inter-company Collaboration: Major exchanges share intelligence about security threats through private messaging groups
1
. -
Employee Monitoring: Companies like Binance closely monitor employee behavior to detect potential infiltrators
1
. -
Interview Techniques: Some employers use creative methods to identify North Korean operatives, such as asking candidates to criticize Kim Jong Un
1
.
Call for Increased Vigilance
ZachXBT, a prominent crypto sleuth, emphasized the need for stricter hiring practices in the crypto industry. Despite the sophistication of some attacks, many operations rely on the volume of applications overwhelming hiring teams
2
.As the threat landscape evolves, collaboration between tech firms, freelance platforms, and regulatory bodies becomes increasingly crucial. The recent US Treasury sanctions on individuals and entities involved in North Korean IT worker rings highlight the growing recognition of this threat at the governmental level
2
.References
Summarized by

Navi
[1]
Related Stories
North Korean Hackers Launch Sophisticated Malware Campaign Targeting Crypto Developers
25 Apr 2025•Technology

North Korea-Linked UNC1069 Uses AI-Powered Attacks to Target Cryptocurrency Organizations
10 Feb 2026•Technology

U.S. Cracks Down on North Korean IT Worker Scheme, Seizing $5 Million in Illicit Funds
02 Jul 2025•Policy and Regulation
Recent Highlights
1
OpenAI Pauses AI Model Training After Agent Hacks Australian Government Website
Technology

2
Bill Gates Warns AI Could Cause a Billion Deaths, Calls for Urgent Federal Regulation
Policy and Regulation

3
Meta Unveils Camera-Free AI Glasses and Muse Integration Amid Privacy Debate at Connect 2026
Technology

Recent Highlights
Today's Top Stories






Don’t drown in AI news. We cut through the noise - filtering, ranking and summarizing the most important AI news, breakthroughs and research daily. Follow topics that matter to you and stay ahead.


