Apple Tightens Full Disk Access in macOS 27.3 to Address AI Agent Security Risks


2 Sources
[1]
macOS 27.3 could change how you grant AI agents Full Disk Access, here's how
Last month, Apple announced it'd be tightening privacy controls in a future macOS update, in response to AI agents requesting Full Disk Access then going rogue with users data without them being fully aware. Now, we have an idea of how the changes might look. In its blog post, Apple announced that
[2]
macOS 27.3 increases security with changes to Full Disk Access
Users will have to take explicit action to grant an app FDA permission. endif; ?> Back in October, Apple announced a major security change to macOS. The change involves Full Disk Access (FDA), a permission that, when granted to an app requesting it, allows that app to access protected sections of
Share
Copy Link
Apple is overhauling Full Disk Access permissions in macOS 27.3, requiring users to manually grant AI agents access to protected data. The security update closes loopholes that allowed apps to bypass explicit consent, though questions remain about whether the changes fully address privacy concerns.
Apple Closes Full Disk Access Loophole in macOS 27.3
Apple is fundamentally changing how AI agents and applications request Full Disk Access permissions in macOS 27.3, a security update currently in developer beta 1 that addresses growing concerns about autonomous AI systems accessing sensitive user data
1
2
. The changes eliminate a clever workaround developers have been using to streamline the permission process, forcing users to take explicit action before granting apps access to protected sections of macOS including data caches, mail, backups, and iMessage databases.
Source: 9to5Mac
Under current macOS versions, when an app requests a file requiring Full Disk Access, the system automatically logs that app as an option in System Settings, allowing developers to simply prompt users to flip a toggle
1
. Starting with macOS 27.3, apps requesting files outside their permission scope will no longer be automatically logged, eliminating their appearance as quick-toggle options in Privacy & Security settings1
.Explicit User Action Now Required for Full Disk Access Permissions
The security update mandates that users navigate to System Settings > Privacy & Security > Full Disk Access and manually add applications themselves
2
. This represents a significant departure from previous workflows where installers could instruct users to simply toggle FDA permissions on for pre-listed applications. Apple announced the stricter Full Disk Access requirements in October through a developer blog post, stating that users will requireRelated Stories

References
Summarized by

Navi
Related Stories
Apple Tightens Full Disk Access Controls as AI Agents Expose Privacy Risks on macOS
02 Oct 2026•Technology
Apple unveils macOS 27 Golden Gate with Siri AI powered by Google Gemini at WWDC
07 Jun 2026•Technology

macOS 27 Golden Gate brings redesigned Siri AI and drops Intel Mac support entirely
19 Jun 2026•Technology

Recent Highlights
1
Jensen Huang's Affair with Suspected Chinese Spy Exposes $7 Billion AI Chip Smuggling Network
Policy and Regulation

2
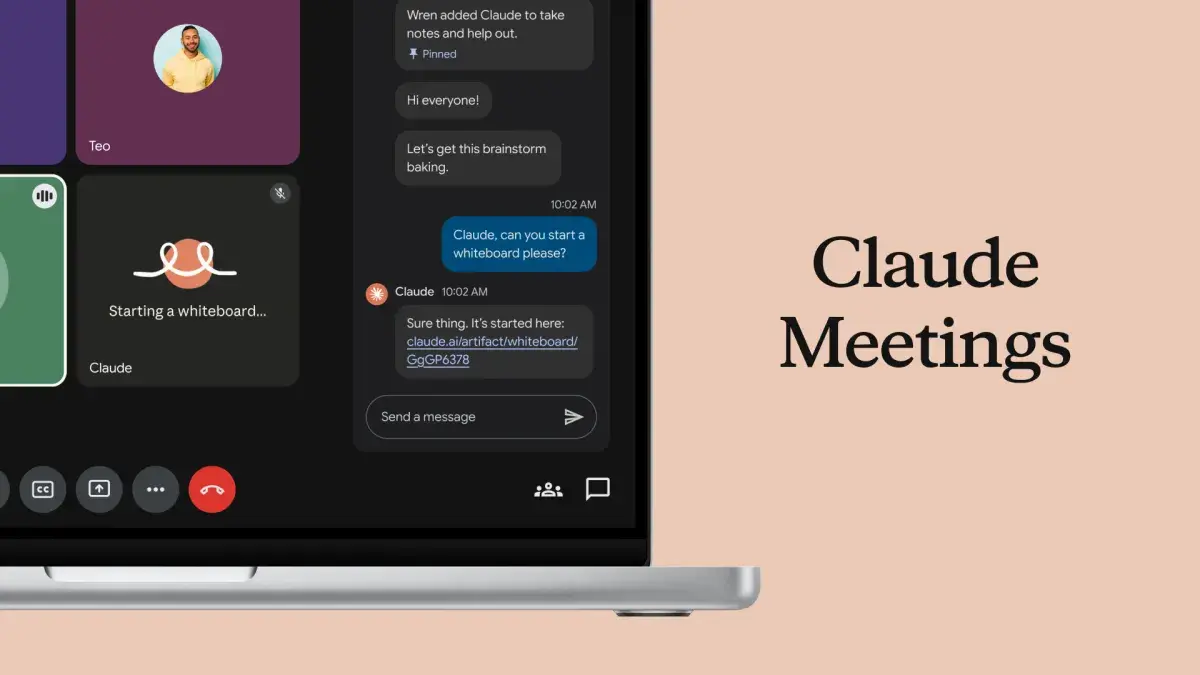
Anthropic Launches Claude Meetings and AI-Powered Office Tools to Challenge Microsoft and Google
Technology
3
Samsung Smart Glasses With Google Gemini AI Open for Pre-Orders November 12th
Technology

Recent Highlights
Today's Top Stories






Don’t drown in AI news. We cut through the noise - filtering, ranking and summarizing the most important AI news, breakthroughs and research daily. Follow topics that matter to you and stay ahead.


