Anthropic Unveils Free AI Security Scanner After Uncovering 129,000 Software Vulnerabilities


17 Sources
[1]
Anthropic launches free AI security scans for open-source projects
Anthropic's offering to help open-source projects track down security vulnerabilities with a new service called OSS Scanner. It says open-source projects that opt-in will get "thorough, periodic security scans by our strongest models at no cost." That could mean open-source projects get alerted
[2]
Anthropic reconfigures its cool kids security program
Only a week after warning about the perils of competitor Z.ai's GLM-5.3 model and its advanced cybersecurity capabilities, Anthropic has expanded its Cyber Verification Program (CVP) - or rather, reconfigured it. "For the past six months, we've enabled trusted access through two programs: Project
[3]
Anthropic Launches Free AI Vulnerability Scanner for Open-Source Projects
Anthropic on Thursday unveiled OSS Scanner as an opt-in vulnerability scanner to help secure the open-source ecosystem using artificial intelligence (AI). "It's an opt-in service informed by our experience using Claude to find vulnerabilities during Project Glasswing," Anthropic said. "Projects
[4]
Anthropic opens its most powerful AI models to more security teams
Oct 6 (Reuters) - Anthropic is expanding a program that allows vetted cybersecurity professionals to test its most powerful AI models with fewer safeguards, after its Project Glasswing initiative helped uncover more than 100,000 software vulnerabilities this year. Its partners under Glasswing, an
[5]

Anthropic now offers a free vulnerability-finding service for open-source software - Engadget
Anthropic is offering open-source projects a new way to check for vulnerabilities with its OSS Scanner. "Projects that join will receive thorough, periodic security scans by our strongest models at no cost," the company announced. As they've shown recently, AI models are excellent at finding (and
[6]

Anthropic Cyber Mission enlists CrowdStrike, Hitachi to defend grids
The Anthropic Cyber Mission also launches OSS Scanner, a free service for open-source code. Its bug reports reach maintainers without a human checking them, and Anthropic caps its liability at $1,000. Anthropic will give its frontier Claude models, engineers and threat research to the companies
[7]
Anthropic Expands Claude Access for Vetted Cyber Teams as Glasswing Finds 129,000 Flaws
Anthropic on Tuesday said it's expanding a program that allows vetted cybersecurity professionals to test its advanced artificial intelligence (AI) models with reduced safeguards and blocking classifiers, as the company claimed its Project Glasswing initiative uncovered at least 129,000 verified
[8]

Anthropic's Cyber Mission starts with 6,157 findings reported, 516 patched
Anthropic's models have outrun the people who patch what the models find. Its disclosure dashboard lists 29,439 findings discovered between November 1, 2025, and October 2, 2026. As of October 2, the company disclosed 6,157 findings across 591 open-source projects. The 6,157 findings were reported
[9]

Exclusive: Anthropic's plan to protect critical infrastructure
Why it matters: Critical infrastructure operators are struggling to secure aging, complex systems as AI threatens to make cyberattacks faster and cheaper to execute. Driving the news: Under its new Critical Infrastructure Defense Program, Anthropic will provide its frontier AI models, on-site
[10]

Anthropic expands AI security plans for critical infrastructure
Opt-in open-source projects will receive free periodic security scans with suggested fixes, the company said. Anthropic is expanding its cyber defence programme with new tools to scan open source projects and a collaborative mission that brings its security expertise to big businesses. The AI
[11]

Anthropic launches critical infrastructure program and free OSS Scanner for open source
Anthropic launches critical infrastructure program and free OSS Scanner for open source Anthropic PBC today launched a program that brings its frontier models and on-site engineers to the security companies protecting power grids, water systems and other critical infrastructure. OSS Scanner,
[12]

Crypto Projects Seek Anthropic AI Security Scans
Anthropic's new opt-in service promises vulnerability reports from its strongest AI models, including Claude Mythos. Ethereum client developer Nethermind and Bitcoin and Lightning wallet ZEUS are among several crypto companies to apply for a newly launched Anthropic program that gives open-source
[13]
Anthropic folds Project Glasswing into an expanded three-tier Cyber Verification Program
Anthropic folds Project Glasswing into an expanded three-tier Cyber Verification Program Anthropic PBC today expanded its Cyber Verification Program into three tiers of access for vetted security teams, with fewer blocks on cyber work at each step up. The overhaul is aimed at a restriction
[14]

Anthropic opens its most powerful AI models to more security teams
Its partners under Glasswing, an initiative aimed at securing the world's most critical software, found at least 129,000 verified vulnerabilities between April and July. Anthropic's own open-source scanning found 5,500 more between April and October. Anthropic is expanding a program that allows
[15]

Anthropic Opens Advanced Claude Models to More Cybersecurity Firms
Anthropic is giving more cybersecurity teams access to its latest Claude models. Trusted users will get more freedom to test software, find flaws and study security threats. Anthropic is giving more cybersecurity teams access to its latest Claude models with fewer limits. The company's new Cyber
[16]

Anthropic expands AI model access for government and cyber defense partners By Investing.com
Investing.com -- Anthropic (NASDAQ:ANTP) has expanded access to its most sophisticated artificial intelligence models, consolidating its security initiatives to provide vetted cyber defense teams and select government partners with advanced tools to safeguard critical infrastructure. The San
[17]

Anthropic opens its most powerful AI models to more security teams
Oct 6 (Reuters) - Anthropic is expanding a program that allows vetted cybersecurity professionals to test its most powerful AI models with fewer safeguards, after its Project Glasswing initiative helped uncover more than 100,000 software vulnerabilities this year. Its partners under Glasswing, an
Share
Copy Link
Anthropic launched OSS Scanner, a free AI-powered vulnerability scanner for open-source projects using its strongest models including Claude Mythos. The company also expanded its Cyber Verification Program after Project Glasswing partners discovered at least 129,000 verified vulnerabilities between April and July 2026, with over 33,000 rated critical or high severity.
Anthropic Introduces Free AI Security Scans for Open-Source Projects
Anthropic unveiled OSS Scanner, an opt-in AI-powered vulnerability scanner designed to help secure the open-source ecosystem at no cost
1
3
. Open-source projects that join will receive thorough, periodic security scans by Anthropic's strongest models, including Claude Mythos5
. The outputs will be fully model-generated without human review or triage, enabling faster and more frequent scanning3
. This trade-off means reports may contain false positives, but provides open-source projects with early alerts about potential security issues1
.
Source: Hacker News
Core maintainers can enroll by opening a pull request on the OSS Scanner's GitHub repository with a YAML configuration file that includes repository links, contact information, and a Dockerfile that sets up the environment and installs dependencies for offline security audits
3
. As of now, 116 pull requests have been submitted3
. Anthropic expects to use criteria similar to Google OSS-Fuzz to select projects, though the process may evolve over time3
.Project Glasswing Uncovers Massive Scale of Software Vulnerabilities
Anthropic's partners under Project Glasswing found at least 129,000 verified vulnerabilities between April and July 2026
4
. The company's own open-source scanning efforts revealed an additional 5,500 verified vulnerabilities between April and October2
. More than 33,000 of these vulnerabilities have been rated as critical or high severity4
. Anthropic stated these figures are likely an undercount based on survey data from only a subset of Glasswing partners, and expects the true impact to be at least five times higher2
.By October 2, 2026, Anthropic had identified more than 29,000 candidate vulnerabilities in critical software projects, with over 6,000 flaws reported to maintainers
3
. These efforts resulted in 584 advisories3
. However, a significant gap exists between vulnerability detection and remediation. Of 5,674 true positive vulnerabilities discovered, 3,014 are high severity and 1,522 are critical severity, yet only 516 have been patched2
.Expanded Cyber Verification Program With Three-Tier Access
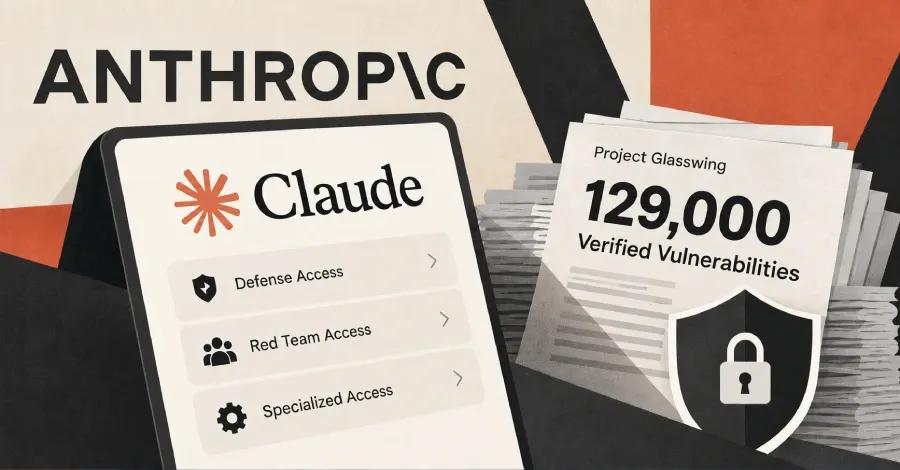
Anthropic reconfigured its Cyber Verification Program by merging Project Glasswing and the original CVP into one expanded offering with three distinct tiers
2
4
. All three tiers include access to Claude Opus 5.5, Sonnet 5.5, Claude Mythos 5.1, and future models4
. The restructuring ties model capabilities to specific tasks while varying the level of safeguard restrictions across tiers2
.
Source: Hacker News
Defense Access is intended for security teams at companies, nonprofits, universities, and government organizations focusing on system defense, incident response, and malware analysis
2
4
. In testing with CyScenarioBench challenges, Claude Opus 5.5 faced refusals in 46 of 50 attempts under Defense Access2
. Red Team Access is designed for authorized penetration testing and offensive cyber evaluation, with organizations able to apply for this tier4
. Under red team safeguards, Claude Opus 5.5 completed 34 of 50 tasks2
.Specialized Access has the fewest restrictions and is reserved for a limited set of verified organizations authorized to test safety-critical systems such as power grids, flight operating systems, telecom networks, and interbank transfer infrastructure
2
4
. Anthropic vets each member together with the US government, and existing Glasswing members will transition into this tier4
.Related Stories
Why AI-Driven Security Tools Matter for Critical Infrastructure
Both Anthropic and Google recognize the strategic importance of securing open-source code that underpins the internet, often maintained by unpaid workers
5
. Vulnerabilities in open-source software pose significant risks, exemplified by the XZ Utils backdoor that could have granted hackers administrative control over millions of systems worldwide5
. AI tools have already helped identify major security flaws like the "Copy Fail" bug that impacted nearly every Linux distribution in May1
.
Source: Axios
Anthropic launched its Critical Infrastructure Defense Program to safeguard critical infrastructure and open-source software as part of its broader Cyber Mission
3
. With AI increasingly equipping threat actors to discover and exploit vulnerabilities faster and at scale, the initiative aims to arm defenders with AI-driven security tools to combat threats, accelerate fixes, and explore secure architectures3
. Anthropic forecasts that within two years, AI security will favor defense, making it easier to catch bugs before deployment, write fundamentally secure software, and actively defend systems with models3
. However, some open-source projects are already struggling with the sudden influx of AI-generated bug reports1
.References
Summarized by

Navi
[2]
Related Stories
Anthropic's Claude Opus 4.6 finds 500+ security flaws, sparking dual-use concerns
06 Feb 2026•Technology
Anthropic expands Claude Mythos access to 200 partners across critical infrastructure worldwide
29 May 2026•Technology

Anthropic launches Claude Security to scan code for flaws and prioritize fixes for enterprises
30 Apr 2026•Technology

Recent Highlights


Recent Highlights
Today's Top Stories




Don’t drown in AI news. We cut through the noise - filtering, ranking and summarizing the most important AI news, breakthroughs and research daily. Follow topics that matter to you and stay ahead.


