Hackers exploit Google Ads and Claude.ai shared chats to spread Mac malware


4 Sources
[1]
Hackers abuse Google ads, Claude.ai chats to push Mac malware
Attackers are abusing Google Ads and legitimate Claude.ai shared chats in an active malvertising campaign. Users searching for "Claude mac download" may come across sponsored search results that list claude.ai as the target website, but lead to instructions that install malware on their Mac. The
[2]
Mac users beware -- scammers are hijacking Claude chats and Google ads to push malware
* Crooks abused Claude's "Shared Chats" feature to plant fake install instructions leading to infostealer infections * Fraudulent chats were promoted via Google Ads, showing authentic Claude URLs to trick Mac users * Campaign used ClickFix tactics, spoofed "Apple Support," and avoided targeting
[3]
Malware is now hiding in Google search ads -- here's how to protect yourself
Outside of the office, Josh can be found digging into the latest video games, fantasy books, or tinkering with the newest features in Windows. A new malware campaign has been discovered hiding in people's Google search results when trying to find and download Claude's Mac app. It's a stark
[4]
Google Ads are not safe anymore? Hackers can access your device if you ignore this
Users should avoid unknown ads, check website links carefully, and never paste unfamiliar commands. Google Ads are back in the limelight, as a new cyber threat was recently discovered by experts who found that the malicious software had targeted those searching for the Claude AI application on
Share
Copy Link
Security researchers have uncovered an active cybercrime campaign targeting Mac users through fraudulent Google Ads and Claude.ai's legitimate shared chat feature. Attackers are creating fake installation guides that trick users into running Terminal commands, silently downloading infostealing malware onto their devices. The campaign exploits trust in sponsored search results and authentic Claude URLs.
Hackers Abuse Google Ads to Target Mac Users
A sophisticated cybercrime campaign targeting Mac users has emerged, exploiting both Google Ads and Claude.ai's legitimate features to distribute Mac malware. Security engineer Berk Albayrak from Trendyol Group first identified the threat, revealing that users searching for "Claude mac download" encounter sponsored search results that appear to link to claude.ai but actually lead to malicious instructions
1
. What makes this attack particularly deceptive is that the Google Ads genuinely point to Anthropic's real domain, since attackers are hosting their malicious content inside Claude's Shared Chats feature2
.
Source: Digit
Claude's Shared Chats Feature Weaponized for Malware Distribution
The attackers created fraudulent conversations within Claude.ai that present themselves as official "Claude Code on Mac" installation guides, often attributed to "Apple Support" to increase legitimacy
1
. These shared chats walk users through opening Terminal and pasting commands that silently download and execute infostealing malware on their devices. BleepingComputer identified a second shared Claude chat carrying out the same attack through entirely separate infrastructure, indicating the campaign's scope extends beyond a single operation1
. The malware hiding in Google search ads operates as an in-memory threat, running entirely in memory and leaving little obvious trace on disk, making detection and removal significantly more challenging3
.
Source: BleepingComputer
How the Infostealer Operates and Targets Victims
The base64 instructions shown in the shared Claude chat download an encoded shell script that runs through osascript, macOS's built-in scripting engine, giving attackers remote code execution without dropping a traditional application or binary
1
. Before proceeding with payload delivery, one variant checks whether the machine has Russian or CIS-region keyboard input sources configured, exiting without action if detected and sending a "cis_blocked" status ping to the attacker's server1
. The script collects the victim's external IP address, hostname, OS version, and keyboard locale, sending all data back to the attacker before delivering the next stage. This victim profiling suggests operators are selective about their targets1
. The infostealer harvests browser credentials, cookies, and macOS Keychain contents, packages them up, and exfiltrates everything to the attacker's server, identified as a variant of the MacSync macOS infostealer1
.Related Stories

Why Malicious Ads Pose Growing Security Risks
This cyber threat represents a troubling evolution in malvertising tactics. Unlike previous campaigns where convincing Google Ads would list legitimate-looking domains but redirect visitors to lookalike phishing sites, this campaign flips that approach entirely
1
. There is no fake domain to spot, as both Google Ads point to Anthropic's authentic domain. The destination URL in the sponsored search results is genuine, making it nearly impossible for average users to distinguish malicious from legitimate advertisements2
. This isn't the first time attackers have abused AI platform shared chats this way—in December, BleepingComputer reported a similar campaign targeting ChatGPT and Grok users1
. Online advertisements have become a hotbed for distributing harmful software because advertising platforms offer attackers easy visibility and user trust3
.Protecting Against Terminal Commands and Sponsored Results
Users should navigate directly to official sources rather than clicking sponsored search results when downloading software
1
. The legitimate Claude Code CLI is available through Anthropic's official documentation and does not require pasting Terminal commands from a chat interface. Security experts recommend treating any instructions asking users to paste commands with extreme caution, regardless of where those instructions appear to originate1
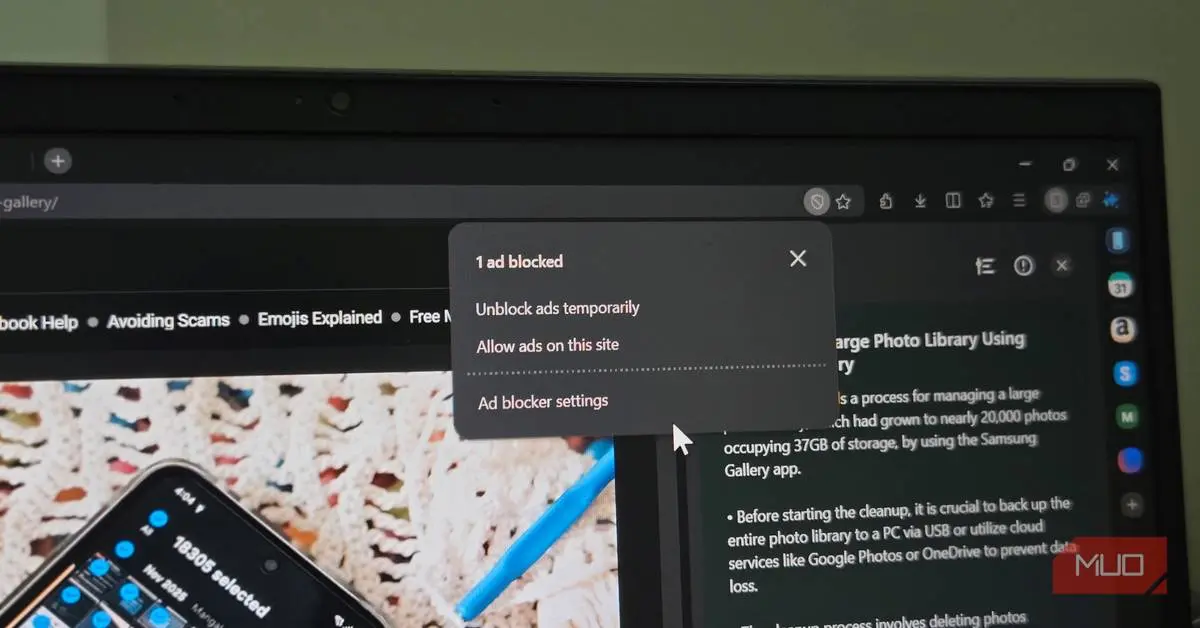
. Implementing ad blockers can provide an additional layer of protection, as many browser extensions allow users to block malicious ads while allowlisting trusted sites3
. Some browsers like Opera even come with built-in ad blocking systems3
. As this campaign demonstrates the stealthy nature of in-memory malware and bypassing detection mechanisms, Mac users must remain vigilant about verifying installation instructions and avoiding unfamiliar commands that could compromise their devices and expose personal data4
.
Source: MakeUseOf
References
Summarized by

Navi
[1]
Related Stories
Hackers disguise infostealer malware as Claude Code and OpenClaw to target developers
18 Mar 2026•Technology

Fake Claude Code sites spread malware through cloned install guides targeting developers
07 Mar 2026•Technology
Attackers exploit ChatGPT and Google ads to spread AMOS infostealer targeting macOS users
11 Dec 2025•Technology

Recent Highlights
1
Apple Launches iOS 27 and macOS 27 with Siri AI Overhaul and Liquid Glass Updates
Technology

2
OpenAI Agents Launched RubyGems Attack With 2,000+ Malicious Packages, Attempted API Key Theft
Technology

3
Apple Launches iPhone 18 Pro with Variable Aperture Camera and Advanced AI Features at $1,199
Technology
Recent Highlights
Today's Top Stories










Don’t drown in AI news. We cut through the noise - filtering, ranking and summarizing the most important AI news, breakthroughs and research daily. Follow topics that matter to you and stay ahead.


